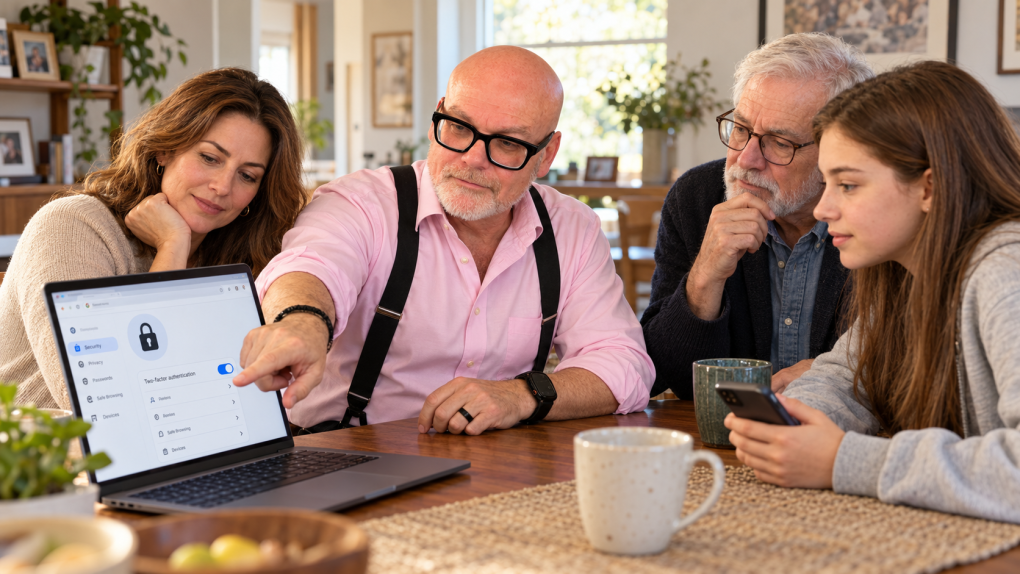
Who are these people?

Everything You Wanted To Ask About Personal Cybersecurity, But Were Not Nerdy Enough To Ask

I was recently asked for some general cyber security advice from a friend looking to help her family and friends during these uncertain times online. In fact, what she actually said was “do you have any good resources/guides you’d recommend on hardening one’s personal security? With what is going on in the world, I want to give me family members something to follow.”

The problems with most advice however is that it has an expiry date. 2-factor authentication was a huge step forward in the securing of personal and work account, but that was 10 years ago. It is still relevant, but there are also many workarounds and deceptive techniques widely employed by criminals that make it a lot less secure now. In fact, whilst most cybersecurity advice sounds straightforward (use strong passwords, switch on multi-factor authentication, keep your devices updated, don’t click suspicious links, etc.), it’s all very specific and frankly a little nerdy.

That is not say that it isn’t sensible advice though, but it can leave you with a rather important question: how do you know what action, message, activity or whatnot looks, and is, suspicious?

A convincing scam might arrive when you are expecting a delivery, worrying about a bill, or waiting to hear from your bank. It doesn’t need to fool you forever, it only needs to catch you at a moment when you are distracted, tired or willing to take something at face value.

Staying safe online therefore involves more than learning a few rules. It means changing how you respond to the things that appear on your screen.

Urgency

The first change is to stop treating urgency as a reason to act.

“Your account will be closed.” “This payment needs approving.” “I need your help right now.” These messages encourage you to make a decision before you have had time to think. Get into the habit of doing the opposite: when a request creates pressure, slow down.

You do not have to establish whether a message is fraudulent before deciding to check it. Open your banking app yourself. Visit the company through a saved bookmark. Call the person using a number you already have. A request can be plausible and still deserve verification.

That also means becoming comfortable with being slightly awkward.

If someone claiming to be from your bank calls, you can end the call and contact the bank yourself. If a relative messages from a new number asking for money, call their usual number. If a colleague sends an unexpected document requiring you to sign in, check with them through another channel.

You are allowed to interrupt the flow of a conversation. You are allowed to say, “I’ll check and get back to you.” You do not owe a stranger immediate cooperation because they sound helpful, authoritative or impatient.

Attraction

The next change is to think less about whether you are an interesting or attractive target.

“I’ve got nothing worth stealing” is a comforting thought, but consider what losing access to your email would mean. What could someone reset? Who could they contact while pretending to be you? Which documents, photographs and conversations could they see?

Your email account deserves particular attention because it can provide a route into other accounts. Give it a unique password and enable multi-factor authentication. Use a password manager to make unique passwords manageable elsewhere, too. These are among the National Cyber Security Centre’s core recommendations.

Think about the consequences of losing access, rather than how valuable you imagine yourself to be.

Routine

It also helps to stop making security depend on remembering to be careful all the time. Nobody maintains perfect concentration. Build habits and settings that carry some of the cognitive load. Enable automatic updates. Let a password manager generate and save passwords. Put a screen lock on your phone. Make backing up important files something that happens automatically.

The NCSC recommends keeping software updated because updates include security fixes. Treat that maintenance as an ordinary part of owning a device, like charging it, rather than an interruption you can postpone indefinitely. (More NCSC guidance )

Apply the same thinking to what you install and share.

Before downloading an app, adding a browser extension or granting access to your contacts, pause long enough to consider whether you need it. Does this service need your date of birth? Does that app need your location all the time? Are you keeping an account you stopped using years ago?

You do not need to become secretive about everything. Simply get used to treating access to your information as something you choose to give.

Failure

Another useful change is to prepare for mistakes.

Could you get back into your accounts if your phone disappeared tomorrow? Do you know where your recovery codes are? Is your recovery email address still accessible? Could you recover the photographs and documents you care about?

Keep backups and occasionally check that you can restore something from them. For an external backup drive, disconnect it when it is not in use. The NCSC’s backup guidance explains why a separate, recoverable copy matters.

Whoops!

Finally, take embarrassment out of the response.

If you think you have been caught, tell someone and act promptly. Contact your bank through a trusted route if money is involved. Secure the affected account. Ask for help if you are unsure what happened.

Make it easy for your friends and family to do the same. A friend group or household where someone can say “I think I’ve made a mistake” without being ridiculed is better prepared to deal with one.

In summary, you don’t need to distrust everything or become a technical expert. You just need a few dependable habits that still work when you are busy, worried or distracted.

  • Slow down when you feel rushed. Pressure is a reason to check before acting.
  • Check through a route you trust. Open the app yourself or call a number you already know.
  • Make protection routine. Use unique passwords, multi-factor authentication and automatic updates.
  • Prepare to lose access. Keep recovery details safe and maintain backups you can restore.
  • Speak up quickly if something goes wrong. Getting help matters more than avoiding embarrassment.
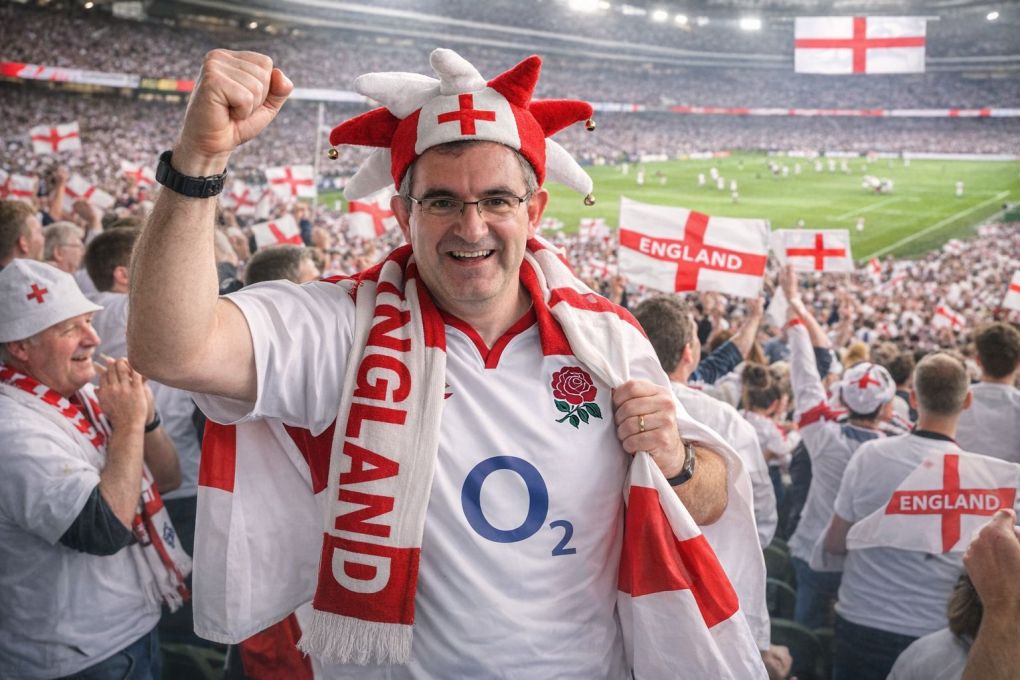
Here is What the Rugby 6 Nations Taught me About B2B Marketing*

(*That LinkedIn post really did spoil it for all of us, didn’t it?)

I’m writing this towards the end of Super Saturday, the final day of the greatest rugby tournament in the world, and with just one match left to play between England and France. Because of vagaries of the way points are earned the final match will decide who is going to win the entire tournament, and it is currently between Ireland and(who just beat Scotland who could have won if they beat Ireland…) and France. If England beat France then Ireland win, and if France beat England then they win. All clear so far?

As you may have gathered from the image above, cybersecurity’s most famous Irishman is therefore supporting England today, and anyone who know Mr Honan will know that he is a regular member of the ABE club. ABE I hear you say? Anyone But England. It’s a small but popular club with members from all of the other nations, so to have a proud Irishman supporting England tonight is both a surprise and a pleasure. (7 – nil to France UGH!)

This may sound like I am complaining about all of the ABE members out there, but also anyone who knows anything about rugby is that actually it is the rugby that is important. Even the most passionate, ardent and patriotic rugby supporter would rather watch a “good” game of rugby between two teams than a game won by their team involving poor play, cheating or just a general bad sportsmanship. Supporting rugby is about just that, it is supporting the game, the play, the ethos, the camaraderie and general improvements of the battle being played on the field. It is one of the reasons why there is no supporter segregation in the rugby grounds or even int he pubs outside. The entire day is a mix of both colour of shirts and lots of drunken hugging, back slapping and general piss-taking. (7 – 5 England score!)

So what does this have to do with Cybersecurity? (14 – 5 to France UGH!) Well, it reminds be of how cybersecurity and organisations deals in secrets all the time, and rightly so. We can’t share IP, we can’t always declare the moment we have an incident, or even declare that we are under attack. (14 – 10 England Score!) However every single cybersecurity professional I know would like nothing more than to share security intelligence with anyone and everyone, even those who may even be in competitive markets to the one that are operating in. (17 – 10 to France. This is painful…)

Why? Because it raises the bar for everyone, makes the dark spaces the criminals operate in harder and more expensive to do so, pushing them away and potentially encouraging them to make better life choices and their Mother’s finally proud of them. (17 – 17 England score and convert!)

(17 – 24 England try and conversion!) This kind of camaraderie, and a desire to see everyone play better, do better, perform better and generally raise the bar for everyone is exactly the spirit that we need across our industry. We will never be able to defend against the massive onslaught from the criminals who are often better funded, motivated and resourced as individuals. We have to group together, aim for the greater good and benefit to everybody and raise the bar for everyone. (17 – 27 England penalty goal!). This is why we “do” security, why we want to get up in the morning, and why we want to collaborate so we can all win against the criminals.

(24 – 27 France penalty try UGH!) It’s halftime, and it has been some of the best rugby I have seen of the entire tournament, and certainly the best that England have played for a long time, and while I know that I am definitely wanting England to win, if nothing else but to save some face from the haters front he last few weeks, the best part is that it has been a great game of rugby between two titans of the game, playing their very best.

And if that means Mr Honan being an honorary Englishman for the evening, I’m here for it.

FULL-TIME UPDATE France 48 – 46 England. Maybe next time Mr Honan.


Taking Care of Business

I remember back in early 1996 arriving home from work and telling the future ex Mrs Langford that was going to be very busy “for the next two to three months”. There was a project going on that I decided I was going to get involved in (outside of my normal IT Manager day job) and that it was going to be good for my career. In modern parlance, I had decided to “lean in”.

Those busy two to three months ended for me on the 10th September 2017. I had pushed myself professionally as hard as I could, burnt the candle at both ends, worked long hours, was only off work sick when I euphemistically “called in dead”, accrued millions of air miles, and was ostensibly successful in my career. Without wishing to dwell here on the events of that fateful night/morning in September 2017, I had reached the end of the line; all of that work and effort had ultimately netted my severe anxiety and stress, diabetes, alcoholism, and a desire to make it all stop very violently.

All of which brings us neatly to right now. I am currently off work sick. I’m very likely to head back tomorrow 9even though I am not 100%, but boredom is a keen medicine sometimes), but I have had the best part of five working days of, plus a weekend in between. I had been feeling under the weather for about a week or so beforehand, but at about midday on my first day off I decided to just switch off my computer and go to bed, and there I more or less stayed for the best part of a week. I had tested positive for COVID, but a few days later that was now negative and I still felt like a bag of rusty spanners had taken residence in my lungs, and my energy levels were depleting like a Death Star tractor beam. Looks like I worked through a second bout of COVID and then got taken down by another virus; but those are details for me and my GP and work HR I guess.

But “SO WHAT?!” I hear you cry? Well, throughout these last few days of being off I made a conscious effort to disconnect from work as much as possible and focus on my recovery. I learnt my lesson those few years back, and realised I needed to get myself back to fitness, despite the many pressing deadlines and meetings I was missing, and the importance of the work I was doing. I focussed on myself and my health as I knew I don’t want to go back too early and jeopardise not only my health but my work performance.

And you know what? Despite everything I had experience before and told myself, I still felt guilty about taking the time out.

This shouldn’t come as a surprise to anybody, anywhere though, not least the information security industry. A few weeks ago, my good friend and all round good chap Sarb Sembhi, who along with Peter Olivier and Paul Simms authored a paper on Mental Health in Cyber Security, and of which I was asked to peer review. I will leave you to read the paper yourself, but the figures in there are both unsurprising as well as making for uncomfortable reading regarding anxiety, depression, anger, alcoholism etc..

I was asked by a client over dinner recently “what keeps you up at night?”. Obviously they were fishing for gossip/insight into the state of our joint business, but I told them that basically nothing does because after my life changing experience back in 2017, I refuse to get stressed or anxious over work matters because it simply isn’t worth it, especially as I am not CISO for something that may save/take lives. And yet here I am feeling guilty about taking maybe another day off sick, and deciding to go back even though I am still not breathing right and feeling fatigued. Surely I should know better?!

To be clear, we are (normally) compensated well and a have privileged positions at work to get the job done properly; we have responsibilities to our colleagues and to the clients and markets we support to do the right job and put the effort in, and frankly most of us even enjoy our jobs. But I can absolutely guarantee you that none of that is worth anxiety, depression, anger, diabetes, alcoholism and suicidal tendencies if that pressure to perform is maintained indefinitely.

Taking care of business ultimately means taking care of yourself first.


I am going to be at InfoSecurity Europe in a few weeks time on stage with the Sarb and Peter, authors of the above mentioned Mental Health in Cyber Security paper.


Links to other interesting stuff on the web (affiliate links)

What Exactly is the Cyber Scheme?

Solving today’s Security Challenges With Device Centric SSE

Sneaky Tricks In Enterprise Pricing


Beer, PowerPoint and Politics

Gone are the days when being a CISO (or even just ‘the security guy/gal’) was about actual information security or IT security. Even the term IT Security is outdated now and emphasises a one-dimensional view of what security is really about. However, I digress…

The Information Security element of CISO is correct, but for various reasons, the CISO’s role is very different from what it was a decade ago. The role then required a strong technologist who understood the firewalls, their rules, the cryptographic controls and even how to code hotfixes on the fly. This isn’t surprising given the role almost wholly came from an IT background; after all, back in the day, mere lip service was paid to the human element, and the legal considerations were considered simply “someone else’s job”.

I was often asked what my job as a CISO entailed, and because I didn’t initially understand what I had actually got myself in for when I took on my first CISO job I used to jokingly say;

PowerPoint and politics

Me. Back Then.

The odd thing is that this response is not far from the truth. My role became significantly less about my understanding of specific niches of information security knowledge and more about putting across to the business what this information security lot was all about and how it helped the company stay competitive, out of trouble or even just in business. The more I was doing this, the more I was embroiled in the day-to-day machinations of how a business works and the inescapable conclusion I came to was this; even if information security is seen as essential to the business, it is still just one voice of many that are trying to influence, cajole and be heard.

Moreover, this is where the politics come in, unfortunately. It is human nature and the way of businesses around the world. Politics is everywhere, and any CISO who doesn’t see and at least understand what is going on is, at best, going to be ignored and, at worst, eaten alive.

Which brings me to my second quote from me (well, it makes attribution a whole lot easier, doesn’t it?);

The purpose of a CISO is not to make the company more secure per se, but rather to help it sell more beer/widgets, increase shareholder value (as appropriate), and let the business make risky decisions more easily… through the judicious use of security

Me, Just now. Again.

The CISO should not be concerned with the name on the front of the firewall or the specifics of the latest penetration test. Instead, they should focus on how best to align their security services to the business and ensure security isn’t just a cost centre but a capability that allows teams and the company to run faster, more efficiently, and with less risk.

That doesn’t take technical knowledge; that takes strategic and business knowledge.

Links to other interesting stuff on the web (affiliate links)

Shift Gears: How to Leverage Data-Centric Security Controls in AWS

Changes to the OWASP API Security Top Ten 2019 to 2023

Cybersecurity as an Operational Effort


CISO Basics, Part 2

In the last post, I looked at some of the less apparent activities upon becoming a new CISO, namely:

  1. Stop thinking that infosec is your business.
  2. Stop making technology purchases.
  3. Ask your vendors to explain what you have in your services inventory.

In this post, we will take this a step further and closer to actual business as usual and maintaining your security team as a functional part of the organisation.

Don’t say “NO!” to everything.

This is an obvious thing to do, but it is much harder to do in practice. The reality is that this requires a complete change in mindset from the traditional view of the everyday CISO. As a species, the CISO is a defensive creature who is often required to back up every decision and be the scapegoat of every mistake (see One CISO, Three Envelopes https://thomlangford.com/2014/12/01/three-envelopes-one-ciso/) and generally rubber-stamp choices that are out of their bailiwick and control.

The mindset shift requires a leap of faith wholly because of this perceived threat of blame and accountability when, in fact, it does just the reverse. 

It starts naturally enough with the language that is used by the CISO and the team, for instance, changing the Change Approval meeting to the Risk Review meeting and not communicating a yes/no or go/no-go response to changes but rather a level of risk associated with the request and alternative approaches as appropriate. There is a need to communicate this shift in the culture, of course, but people will see that they are accountable for decisions that affect the business, not the security team. Shifting the mindset away from being a gatekeeper to a security team that provides sensible and straightforward advice based upon clearly understood risk criteria is a fundamental step towards avoiding being known as the Business Prevention Unit. Politely correct other’s language when they mention an action that requires sign-off or approval from “Security” and help them understand their role in the business decision.

This approach does not require a snap of the fingers for 50% of the problems to go away. Still, carefully planning and educating your stakeholders alters the impact you can have on the business dramatically for the better. It also allows you to more easily draw a line between the activities of the security team and the company’s performance, all for the price of merely no longer saying “no”.

Stop Testing Your Perimeter

What? Are you serious?! 

Absolutely.

As you enter a new environment, you will be taking many critical pieces of information on trust and from people with vested interests in their careers, livelihoods and reputations. Your arrival upsets the status quo and has the potential to disrupt the equilibrium; all reasons to not always be forthcoming with every piece of information you request. It isn’t about people being dishonest or deliberately misleading you, but merely being complex, multi-faceted human beings with multiple drivers and influences.

Your perimeter is one of the fundamental pieces of your information security puzzle. Despite cries of “the perimeter is dead”, it remains a prominent place for attacks to happen and where you should feel fully confident that you know every node in that environment to the best of your ability.

Whatever your testing cycle is, suspend it for some time and conduct as complete an investigation as possible into precisely what your perimeter comprises. It can be done automatically with discovery tools, manually through interviews with those responsible, visually in data centres (where you have old school “tin” still being used, and any combination of the above. You will likely find devices that you, and probably existing team members, weren’t aware of, especially with the proliferation of the Internet of Things devices being used throughout the enterprise now. Did facilities install a new access control system or room booking system? Did they consult IT, or more to the point, you?

It sounds like the stuff of legend or the script to the Ocean’s 11 movies, but do you remember when a Las Vegas casino was broken into… through their fish tank? Knowing what devices are where on your network and perimeter is vital and must be considered table stakes in any decent security programme. An alternative is simply a form of security theatre that gives the impression of security and does nothing but create a false sense of security. A cycle of no testing is worth discovering what you don’t know because you can do something about it.

Building your plan

Now you have a grip on your environment in a relatively straightforward, simple, effective and quick way. Through this process, you will ascertain your stakeholders, advocates and even a few potential adversaries. Then, armed with this information, you can provide an accurate picture of the business to the business in a way that makes sense and displays a grasp of the fundamentals.

Building your plan will always start with your initial assessment and what needs to be done to become operational or steady-state. The trick, however, is to ensure that this baseline achievement is perceived as the end state of security but rather merely the first stepping stone to ever more impressive services, capabilities and ultimately, profit and growth for the company.

The plan itself, however? That is yours and yours alone. Although other posts in this Blog will help as you plot your course into the future, nothing will replace your understanding of the local culture, organisation and, ultimately, what you need to achieve to meet the expectations of the business leadership. Know what the rules of your organisation are, when to adhere to them, when to bend them, and most importantly, when to break them (but only when experience tells you it is the right thing to do):

“The young man knows the rules, but the old man knows the exceptions.” 

Oliver Wendell Holmes

Be the Old Man, be the CISO.

Links to other interesting stuff on the web (affiliate links)

5 Ways Penetration Testing Reduces Overall Security Costs

Avoiding Security Theater: When is a “Critical” Really a Critical?

Game of Life Security and Compliance Edition