Charlie & Lola’s Information Security Adventure

lauren_childBeing a frequent traveller, be it train, bus, car or plane, I often get to see people working in all of these environments to one extent or another. From seeing people’s laptops on the front seat of their cars to leaving them unattended in travel lounges, I have seen all sorts of behaviour that we, as information security professionals, would see as unforgivable. We regularly question ourselves as to why this happens, especially when the effects can be so dramatic and have direct impacts on our professional and personal lives.

My most recent example was just last week, sitting opposite a woman who was working on her laptop and referring to a sheaf of A3 colourful papers. They had the unmistakable artwork of Lauren Child, a children’s author and illustrator. As a father of a ten year old and an eight year I recognised the artwork and style immediately as the author of Charlie and Lola, some of my children’s favourite story characters. The papers in questions had plenty of hand drawn mark up on them suggesting this was in the final stages of editing and layout prior to printing, the story itself centering around one Elmore Green who was jealous at the arrival of a younger sibling into his family. It all ends well of course, with Elmore having someone to snuggle with at the end of  the book.

Three things surprised me. Firstly, the way in which the papers in question were left out of the direct sight of the woman concerned, either on a seat on the opposite side of the walkway, or even underneath her own seat (and very accessible from behind). Secondly I was able to discern a large amount of detail from the book in a very short period of time; this is of course partly down to the nature of the book itself, but also, because each page was carefully moved to in turn and then placed somewhere I could review it and even photograph it. Finally, I was alarmed that someone like Lauren Child, who has a very unique and successful place in children’s literature would allow an as yet unpublished book be revealed in public in such a way as this.
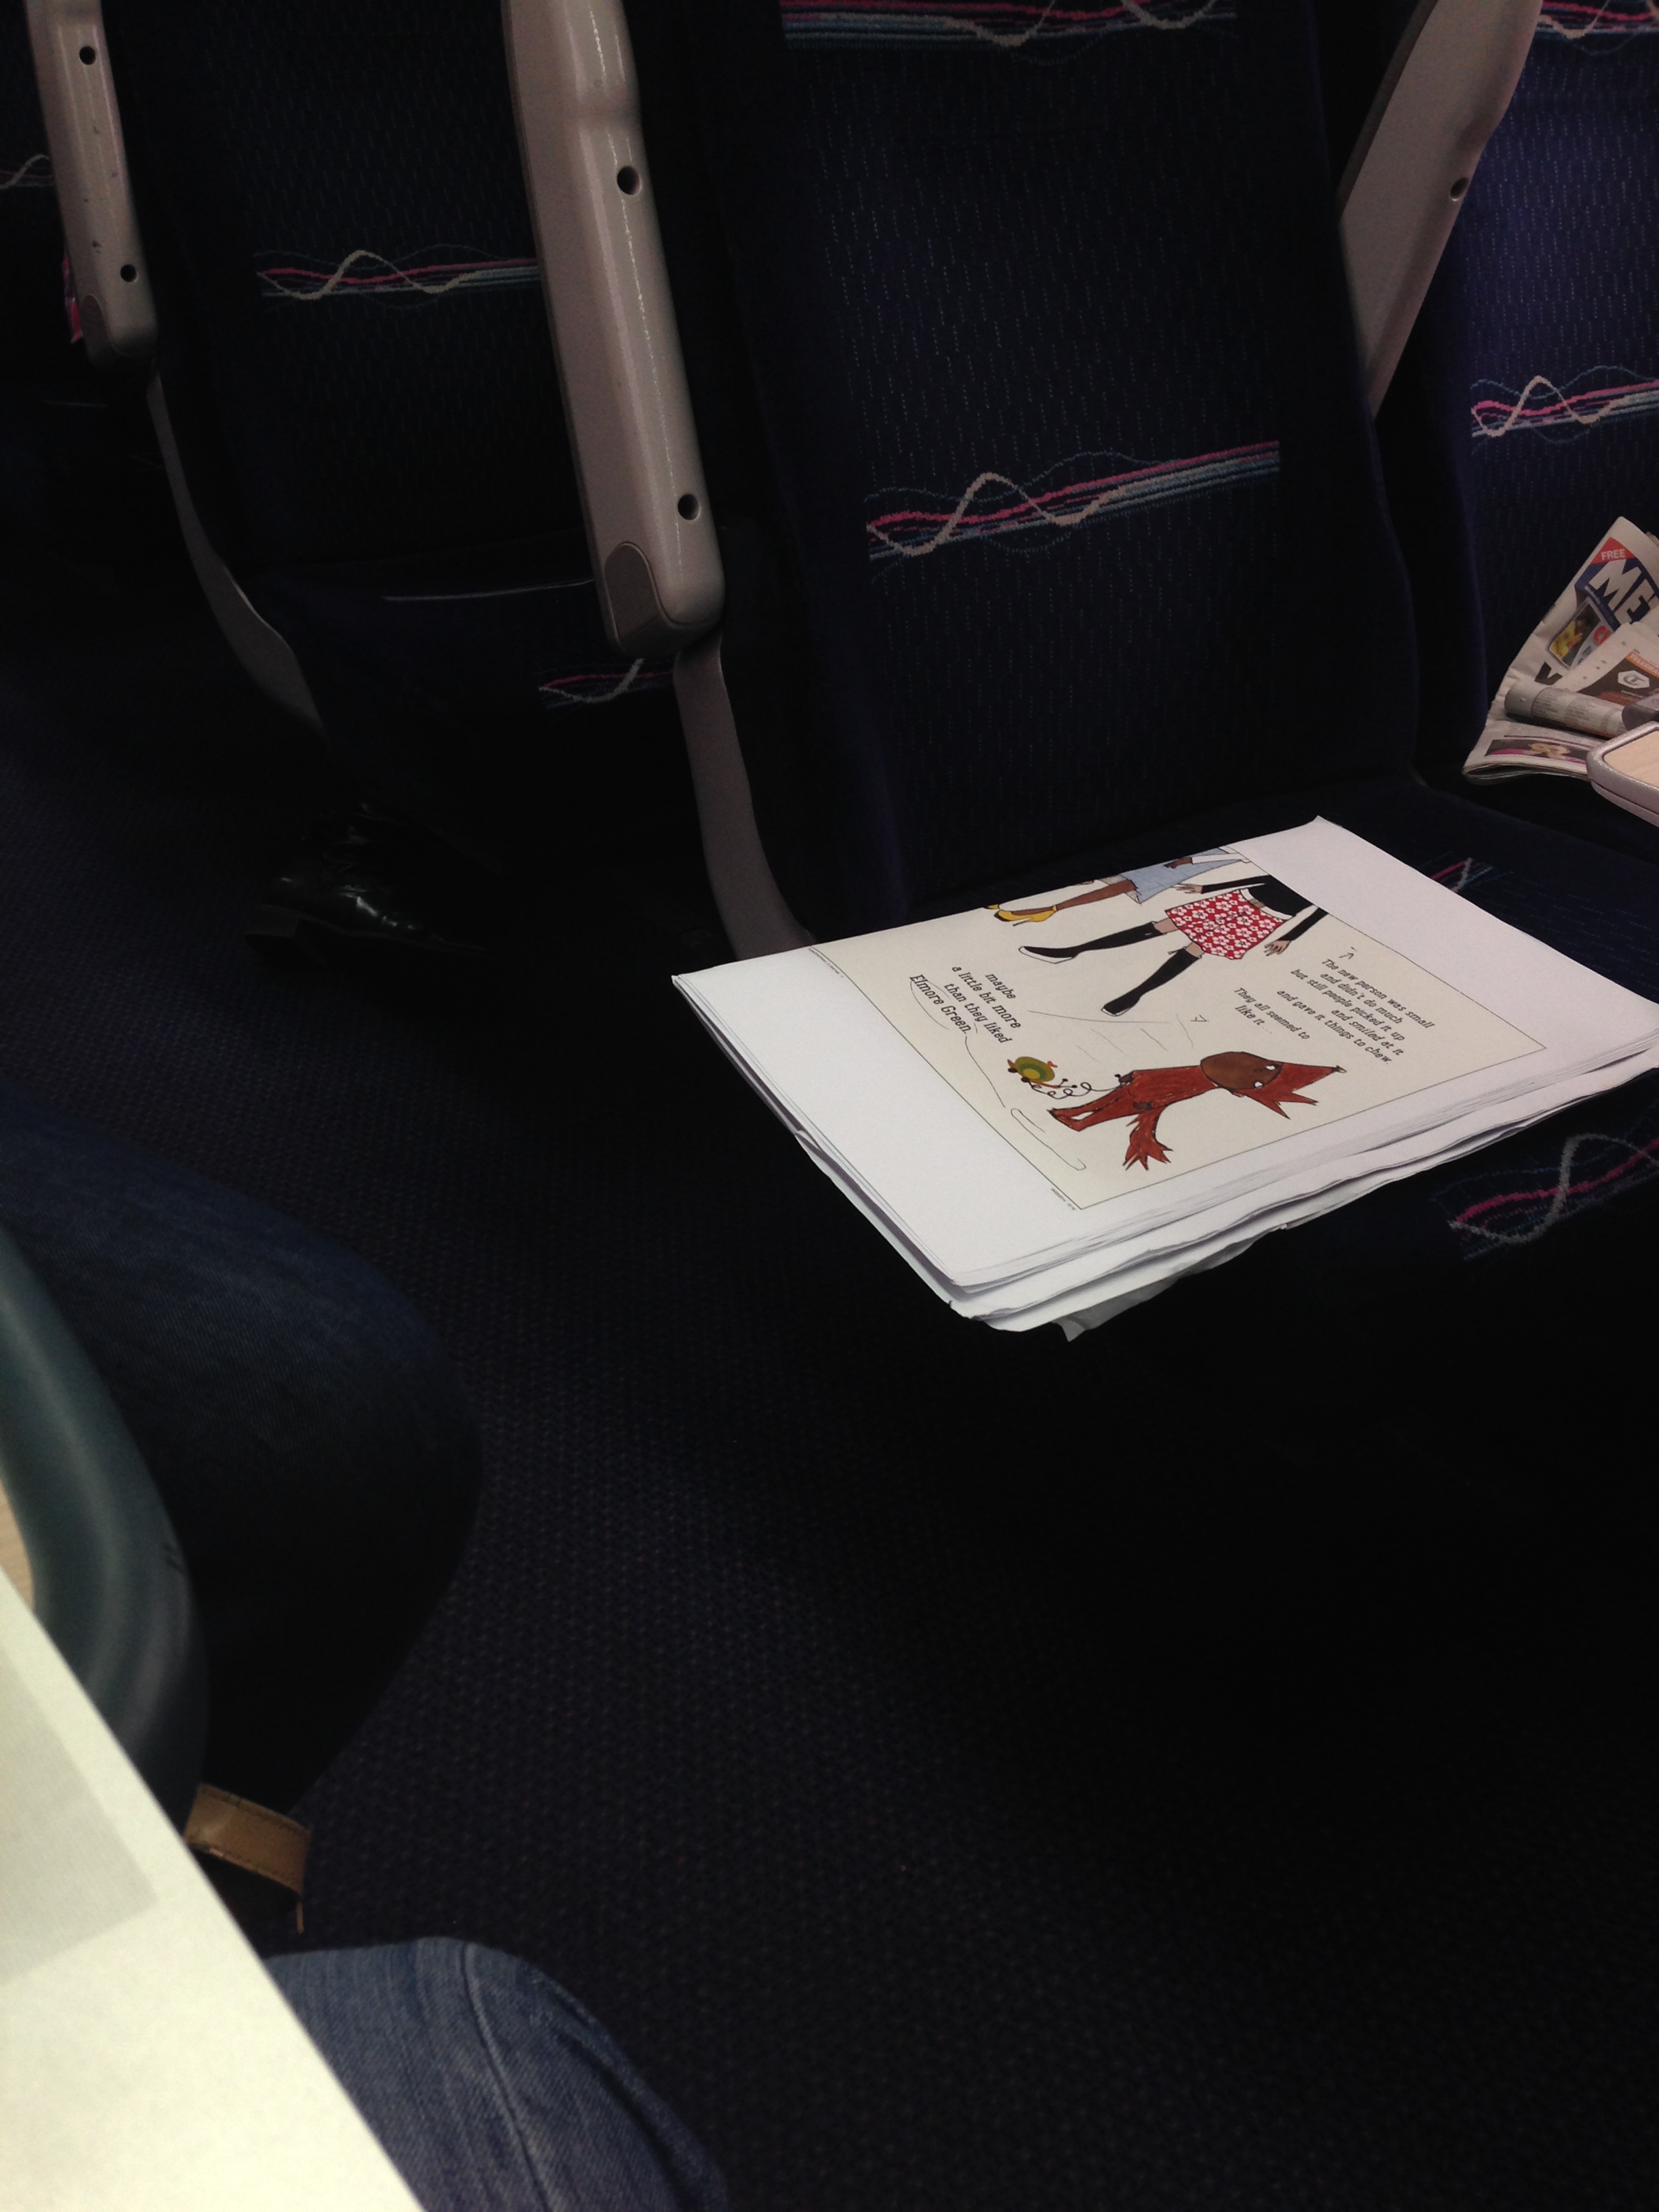
Fingers crossed for Elmore Green!

Fingers crossed for Elmore Green!

This is of course very serious for Lauren Child and her publishers; why was this person allowed to take large copies of this book into a public space? If they knew it needed to be worked on in a train or other public space why weren’t electronic versions made available? Or had they even considered the fact that someone could have easily stolen the manuscript and copied it for an earlier release to capture their particular market?

The implications for UK PLC are probably not that great, and yet examples like this are played out across the country whenever people travel and feel they are in ‘safe‘ environments, with a dangerous cumulative effect for the country. The combined effect of actions like this could potentially add up to the millions in lost opportunities and lost work.  It reminded me of Wendy Nather’s response to a question about public apathy to security, and her surprising yet eerily accurate response was;

I don’t think that society in general will stand up and do something about security until people start dying in enough numbers that it could happen to them individually and not just organizations because we don’t care about organizations.

I sincerely hope Lauren Child has not been hurt by this incident financially or otherwise, she has given too much joy to my children to wish that; but if she reads this I do hope she feels sufficiently motivated to insist on stronger controls around the management of her manuscripts from her publishers.  If you would like some help doing that Lauren, feel free to contact me!

If It is Too Good To Be True, It Probably Is – Cross Post

(Originally Posted on Information Security Buzz on 15 January 2014)

There are plenty of tips on the internet that give great advice on how to avoid phishing scams, and there will be other authors on this site that will be giving very similar advice. For me though, it always comes down to the following three thoughts that I keep in mind whenever I see an email that could possible lead to a scam.

1. Is it too good to be true?

Infosecurity-Buzz-January-2014.002.jpg.001-300x168If the email in question is offering me something for nothing, especially if there is money, or a monetary value involved, this type of email falls into the “too good to be true” category. I have yet to come across an example of when someone really was giving away iPad’s, cash or holidays without some kind of quid pro quo involved. If your answer to the above question even looks like it might be a “yes”, the email and its contents can probably be ignored.

2. Don’t Click it!

Infosecurity-Buzz-January-2014.002.jpg.002-300x168I have borrowed this particular phrase from Jaded Security who coined it a few years ago, and I like it because to be honest it is simple and memorable advice. There are nuances to this of course, but unless you are experienced just don’t click links in your email (see number three). As you get used to looking out for this kind of email there will of course be other telltales that will help you know if an email is genuine or not. For instance, is the email from a close friend, but they haven’t addressed you by your nickname, and seem to be oddly formal, or have more spelling mistakes (or even not enough) in their message? It could be that they have been compromised and you are in their address book and therefore being targeted.

Some people regularly send links in emails, others almost never; if that’s the case, ask yourself why they have suddenly started today seining you a link to a sneezing panda clip.

Finally, if your bank sends you a link to change your password because of system upgrades, don’t click the link they send, but go to your usual bookmark for them. Your bank should never do this anyway, but clicking on a link in an email like this is almost guaranteed to not send you to your bank, but a very convincing fake site set up to harvest your usernames and passwords. Just don’t click it.

3. Fail Safe

Infosecurity-Buzz-January-2014.002.jpg.003-300x168It is always better to mistake a genuine email for a scam rather than the other way around. The consequences of clicking something are very serious whereas the consequences of not clicking on the attached link are rarely, if ever, serious. Additionally, if it is a genuine request, the sender is likely to send a reminder or contact you through another medium such as SMS, letter or telephone. Of course there are plenty of scams through these mediums too (another topic perhaps?), but you will have the balance of probabilities on your side, and the knowledge you haven’t done anything stupid.


Top Five From RSA USA 2014

rsac2014-program-guide-cover-320x407pxI attended the RSA Conference USA last week and was able to witness the chaos, FUD, genuine insight, original thoughts and 25,000 people queueing for a coffee and bagel at 10 o’clock in the morning.

Rather than even attempt to do an end of show round up that other have been able to do far more successfully than me, here are the five things that I remembered the most from the week:

3M Visual Privacy

I still think 3M produce the best privacy filters for monitors, but I have been waiting a long time for technology to catch up and remove the unsightly and easily-left-behind at home piece of plastic in favour of a solution built into the screen itself. Whilst I didn’t unfortunately see that, one of the product managers assured me that this is exactly what the boffins at 3M are currently working on. This is going to be a huge step towards universal and transparent (forgive me) visual security for people using laptops in public places.

MISD_PrivacyFilters_Apple_IMG_ENWW3M also surprised me by demonstrating a pice of software they have designed as well; the known problem with privacy filters is that they only protect you from people looking at your screen from your left or right. From directly behind you they can easily see your screen. The software uses the built in webcam to recognise the users face, and if another face appears in the background looking at the screen, pops up a warning to the user and blurs the screen. To be honest it was a little clunky when I saw it, and it is currently only being developed for Windows, but this is exactly the sort of environment that people working with sensitive information need to “watch their backs” almost literally. I hope they continue to refine the software and expound it to all other major platforms.

Security Bloggers Meetup

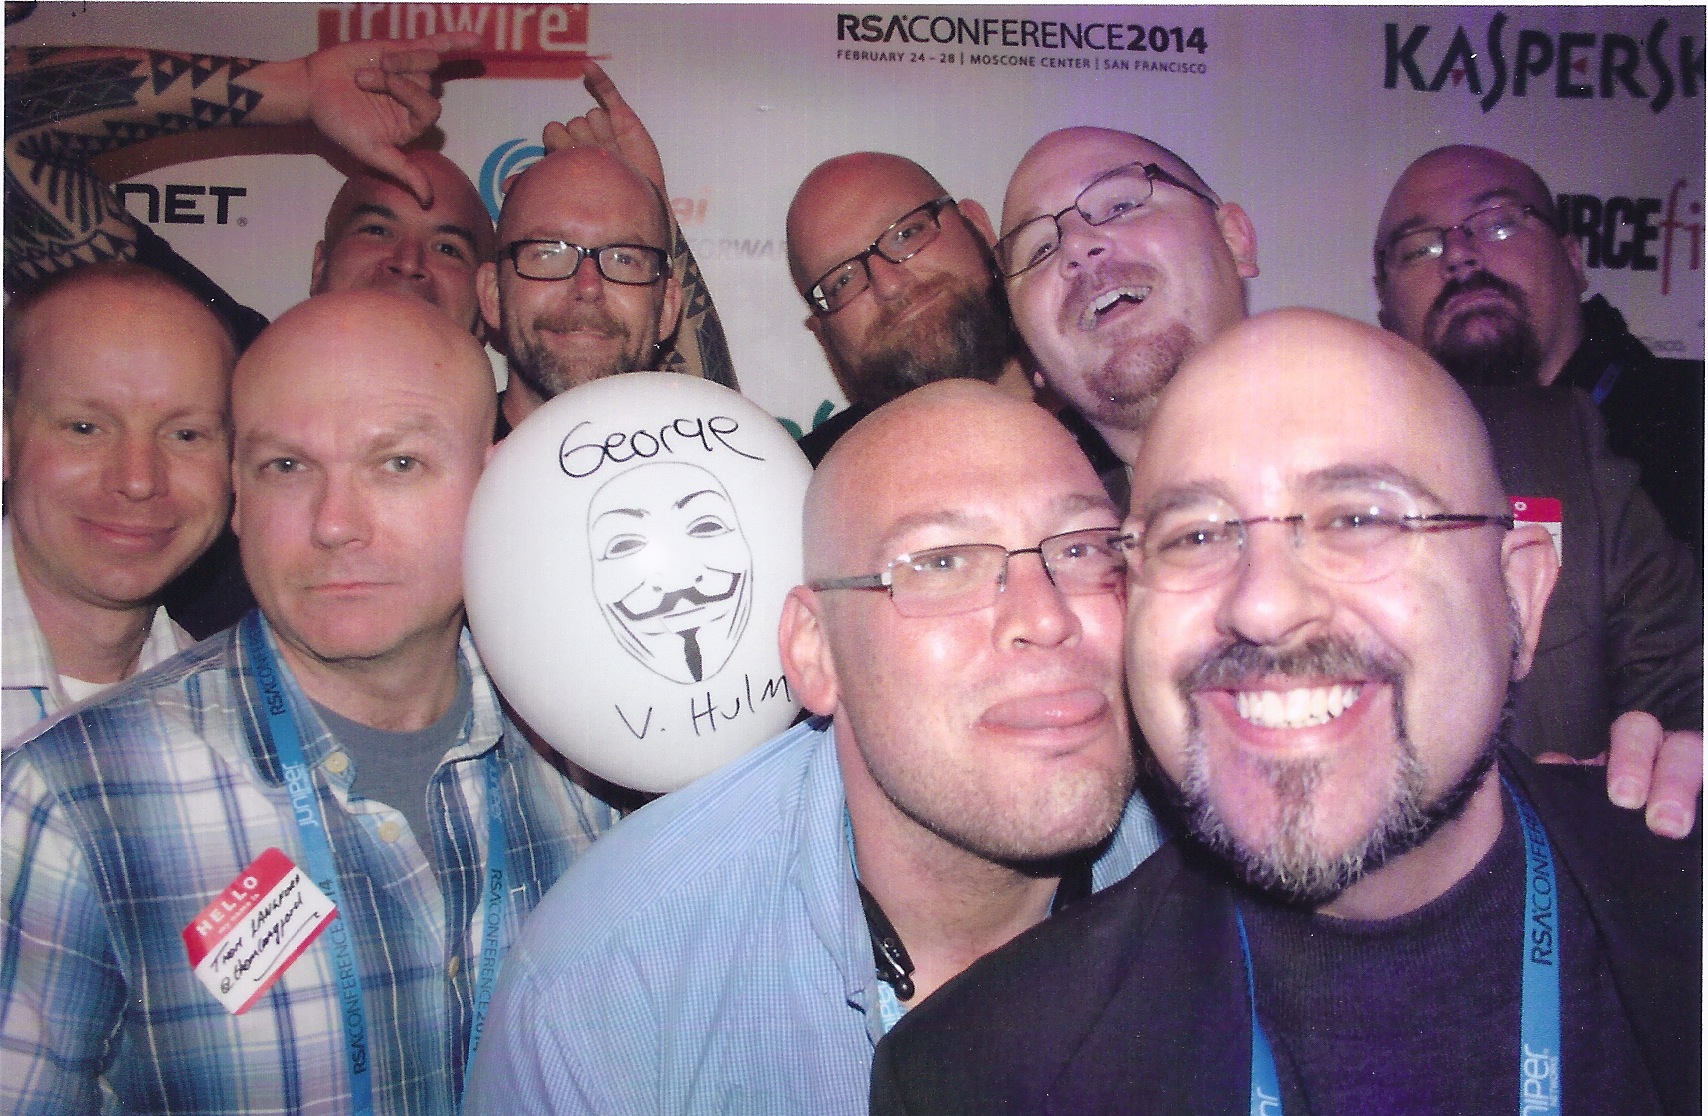
sbnRSAC USA sees the annual meet up of the Security Bloggers Network, so i was very excited to be able to attend this year and witness the awards show and a great deal of silliness and nonsense (to whit, the “bald men of InfoSec” picture for one). I managed to meet for the first time a whole bunch of people that I have either conversed with or followed myself, and some of whom I have very much admired. No name dropping I am afraid as there is too much of that later on in this post, but one thing I did take away was that there is a very valid desire to harmonise the North American and European Security Blogger Awards moving forwards which can only be a good thing and build the international blogger network further. In fact, you can now nominate for the EU Security Bloggers awards here.

The "infamous" bald men of security.

The “infamous” bald men of security.

SnoopWall and Miss Teen USA

snoopwall-website-logoIt wouldn’t be a security conference without some kind of booth babe furore and this one was no different. Although the presence of booth babes has dramatically reduced over the last few years there were still a few vendors insisting on using them. And then we thought we had hit a new time low with the presence of Miss teen USA, Cassidy Wolf, at the SnoopWall booth in the South Hall. Condemnation was rapid and harsh. BUT WAIT… THERE’S MORE TO THIS STORY THAN MEETS THE EYE! After I retweeted my feelings about a teens presence at a conference that could best be described as a recovering alcoholic when it come misogyny, I was contacted by Patrick Rafter, the owner VP of Marketing of SnoopWall.

They have partnered with Cassidy to promote privacy amongst teens in complement to their product that detects the misuse of, for instance, the webcam on your computer or your phone. For those that may not know, Cassidy was the victim of blackmail from an ex classmate who hacked into her webcam in her bedroom, took photos and then demanded more pictures. It goes without saying she stood up to the blackmailer, and has since made privacy one of her “causes” during her tenure as Miss Teen USA. Was having her at their booth at RSA a little misjudged? Yes. Is their cause and campaign (and software for that matter) actually have very good intentions? Absolutely. I chatted with Patrick a day later and while he acknowledged how Cassidy’s presence could have been misinterpreted, he strongly defended her presence and her intentions. I honestly found it laudable. Hopefully over the next few years as the industry finally sorts out its booth babe problem, people like me won’t be jumping to the wrong conclusions as we assume the worst.

The Thomas Scoring System

Thomas Scoring System LogoA few months ago I posted about Russell Thomas’ approach to risk management. I had the good fortune to meet with Russell at the Security Bloggers Meet Up and chatted in depth about his approach to measuring risk consistently. He has turned this idea into a very practical approach via an Excel spreadsheet, a point I made in my earlier review. This is important because without a way to implement at a very practical level it remains a theory. The following day Russell was kind enough to walk me through how to use the system in practical terms, and I am going to be trying it out in my day job as soon as possible. I would urge you to take a look at the Thomas Scoring System as I strongly believe it is a great way of bringing metrics together in a meaningful way.

Gene Kim & The Phoenix Project

I was fortunate enough to have been introduced to Gene Kim, the founder of Tripwire, author, DevOps enthusiast and all round genius/nice guy a few months ago, and we had chatted a couple of times over Skype. (Gene is very generously offering me his guidance around writing a book and his experiences publishing it; yes you heard it here first folks, I intend to write a book!) Knowing he was at RSA I was able to seek him out, and I can now say I have met one of my InfoSec heroes. He is a genuinely charming, funny and generous guy, and he was good enough to sign a copy of his book, The Phoenix project, as well as allow me to get a selfie with him. I would strongly encourage everyone in this field, as well as many of those not in it to read The Phoenix Project, as it quite literally changed the way I looked at the role of InfoSec in a business, and that wasn’t even the main thrust of the book.

Gene very graciously allowing me to take a selfie with him

Gene very graciously allowing me to take a selfie with him

It has taken me nearly a week to recover from RSA, but despite the scandal and boycotts and minor demonstrations it was an excellent conference, as much for the presentations as the “hallway track”. As always, my thanks to Javvad for being my conference wing man again.

Is that Javvad, or a waxwork I am posing with?

Is that Javvad, or a waxwork I am posing with?

Now it is back to real life.


Do as I say, not as I do (and other things our parents told us)

clip-image0026This may be quite a challenging post as I potentially expose myself as a willing victim of an Orwellian world, if not a supporter of it. Nothing could be further from the truth, but I do think certain aspects of the forthcoming argument need to be aired.

I am amazed that people are surprised and angered to hear that the US and UK governments are “spying” on their citizens. I recall as a schoolboy in Dover in the eighties seeing a large installation on the cliffs of Dover, and it was common knowledge that it was used to intercept telephone and radio signals for the government. The thought was, and still is, a comforting one that various powers-that-be are intercepting communications in a morally correct albeit secretive manner.

While the scale of the interceptions highlighted through the Snowden leaks did somewhat surprise me, the fact that it was happening did not, in fact I expected it. My surprise was  perhaps a factor of the rapid growth of the internet and the related technologies, but I was able to rationalise that with the many different methods of communications available to so many people on the planet.

I don’t agree with government back doors inside industry systems, and I don’t agree with the wholesale handing over of encryption keys to them either, but I do agree with the discrete and specific targeting of certain communications of “interest” and the decryption and handing over of those communications by the relevant company to the government in response to a valid and legal request. But it has to start with the interception, analysis, trending and prediction of traffic in the first place.

There, I said it.

We then move to the current advice being given to parents about monitoring and controlling their internet access and social media use. This type of advice is warmly embraced by most people, as one would expect, because children cannot possible be expected to know and understand the types of threats they might be exposed to on the internet, and too naïve to be able to deal with them. They do not have the experience or understanding of what could happen if they use the internet without some kind of supervision and monitoring, and as responsible parents we are there to protect, educate and support.

I think there is a parallel here, namely that the general population simply does not understand the kind of threats that are out there, and how monitoring communications and the internet is a fundamental way of ensuring that we don’t find out the hard way. There has to be a certain level of trust in the various government bodies that the monitoring is done for specific purposes, in the same way a child will have a level of trust that a parent monitoring contacts and online activity is doing so not to harm the child but to protect them from needless abuse and worse.

This parallel is not a clear one I understand; there have been abuses of power, and the politics of government is a dirty business at the best of times, but I pay taxes and participate in my community for the benefit of the greater good and therefore expect a certain level of protection from the powers that be. I chose to live in a somewhat paternalistic society because it benefits me and I get to enjoy a largely violence free lifestyle as a result.

Were you surprised by these revelations? Angered or resigned to them? I will continue to encrypt my most personal of data and practise good information security next time i do my banking in a Starbucks; not to protect myself from the government but from the criminals. I will leave the criminals to the government.


Video: Playing the Game of Thrones at RSA Europe 2013

I’m no HBO, but I am pleased to say I have just posted a video of my talk at RSA onto YouTube, entitled “Playing the Game of Thrones; Ensuring the CISO’s Role at the King’s Table. Recorded by my good friend and evil twin brother Kai Roer (@kairoer) it is the session in its entirety along with pertinent slides throughout.

I was pleased with my personal performance at the time, but of course watching it I see many areas I could improve upon. (I am planting my feet better, but still by no means do I stand still for instance.) The staging of the room was very poor, but unfortunately there was not a lot that could be done about that, and many other speakers had to put up with the same issues.

The full abstract for the talk (from the initial submission) is:

Why is is the CISO constantly frsutrated with being required to report to areas of the business that either don’t understand it or conflict with so many of the core deliverables of the role? Too often it is beholden to the agenda of the technology focussed CIO or blinkered by the financial constraints of the CFO. How has the role even got to this place?

Starting with a brief historical look at where the CISO role was borne from in the first place, progression to this current state of affairs is shown to be inevitable.  What is needed is a plan to disrupt this status quo and ensure a CISO is in a position to not only understand the power of the business intelligence that is produced in a well managed environment, but how to ensure it reaches the board in a way that is understood.

Through the use of a universally understood information security model, the CIA triangle, the presentation explores three key areas to assure the success of the CISO in being asked to report to the board rather than being summoned to it.

Initially the actual source of the information, its gathering, the methods employed and the common pitfalls often seen are explored and clarified. What are the common mistakes, how are they rectified and how can you recognise when the data gathering programme is going awry?

Secondly, how is it being pulled together, and what is it saying? How to understand the audience it is being presented to and what can be done to improve its chances of being understood.

Finally, how does the CISO make the final push for the board? What are the key principles that need to be understood about supporting a successful business, what home truths about the information security industry are rarely mentioned and how can the CISO differentiate themselves from those that came before?

This presentation seeks to broaden a CISO’s skills beyond the technical and the post nominal focussed industry accepted norms and into those that actually help a business do what it does best.

The content from this and my other recent talks will start to appear on this blog as I put my ideas down more into the written word rather than a presentation format. I have just one more speaking engagement before the end of the year now, and one in the first two weeks of the new year, so I hope to find more time to write rather than created decks.

I hope you enjoy the video, and as always I would greatly appreciate your feedback both positive and negative/constructive.