Who are these people?

Everything You Wanted To Ask About Personal Cybersecurity, But Were Not Nerdy Enough To Ask

I was recently asked for some general cyber security advice from a friend looking to help her family and friends during these uncertain times online. In fact, what she actually said was “do you have any good resources/guides you’d recommend on hardening one’s personal security? With what is going on in the world, I want to give me family members something to follow.”

The problems with most advice however is that it has an expiry date. 2-factor authentication was a huge step forward in the securing of personal and work account, but that was 10 years ago. It is still relevant, but there are also many workarounds and deceptive techniques widely employed by criminals that make it a lot less secure now. In fact, whilst most cybersecurity advice sounds straightforward (use strong passwords, switch on multi-factor authentication, keep your devices updated, don’t click suspicious links, etc.), it’s all very specific and frankly a little nerdy.

That is not say that it isn’t sensible advice though, but it can leave you with a rather important question: how do you know what action, message, activity or whatnot looks, and is, suspicious?

A convincing scam might arrive when you are expecting a delivery, worrying about a bill, or waiting to hear from your bank. It doesn’t need to fool you forever, it only needs to catch you at a moment when you are distracted, tired or willing to take something at face value.

Staying safe online therefore involves more than learning a few rules. It means changing how you respond to the things that appear on your screen.

Urgency

The first change is to stop treating urgency as a reason to act.

“Your account will be closed.” “This payment needs approving.” “I need your help right now.” These messages encourage you to make a decision before you have had time to think. Get into the habit of doing the opposite: when a request creates pressure, slow down.

You do not have to establish whether a message is fraudulent before deciding to check it. Open your banking app yourself. Visit the company through a saved bookmark. Call the person using a number you already have. A request can be plausible and still deserve verification.

That also means becoming comfortable with being slightly awkward.

If someone claiming to be from your bank calls, you can end the call and contact the bank yourself. If a relative messages from a new number asking for money, call their usual number. If a colleague sends an unexpected document requiring you to sign in, check with them through another channel.

You are allowed to interrupt the flow of a conversation. You are allowed to say, “I’ll check and get back to you.” You do not owe a stranger immediate cooperation because they sound helpful, authoritative or impatient.

Attraction

The next change is to think less about whether you are an interesting or attractive target.

“I’ve got nothing worth stealing” is a comforting thought, but consider what losing access to your email would mean. What could someone reset? Who could they contact while pretending to be you? Which documents, photographs and conversations could they see?

Your email account deserves particular attention because it can provide a route into other accounts. Give it a unique password and enable multi-factor authentication. Use a password manager to make unique passwords manageable elsewhere, too. These are among the National Cyber Security Centre’s core recommendations.

Think about the consequences of losing access, rather than how valuable you imagine yourself to be.

Routine

It also helps to stop making security depend on remembering to be careful all the time. Nobody maintains perfect concentration. Build habits and settings that carry some of the cognitive load. Enable automatic updates. Let a password manager generate and save passwords. Put a screen lock on your phone. Make backing up important files something that happens automatically.

The NCSC recommends keeping software updated because updates include security fixes. Treat that maintenance as an ordinary part of owning a device, like charging it, rather than an interruption you can postpone indefinitely. (More NCSC guidance )

Apply the same thinking to what you install and share.

Before downloading an app, adding a browser extension or granting access to your contacts, pause long enough to consider whether you need it. Does this service need your date of birth? Does that app need your location all the time? Are you keeping an account you stopped using years ago?

You do not need to become secretive about everything. Simply get used to treating access to your information as something you choose to give.

Failure

Another useful change is to prepare for mistakes.

Could you get back into your accounts if your phone disappeared tomorrow? Do you know where your recovery codes are? Is your recovery email address still accessible? Could you recover the photographs and documents you care about?

Keep backups and occasionally check that you can restore something from them. For an external backup drive, disconnect it when it is not in use. The NCSC’s backup guidance explains why a separate, recoverable copy matters.

Whoops!

Finally, take embarrassment out of the response.

If you think you have been caught, tell someone and act promptly. Contact your bank through a trusted route if money is involved. Secure the affected account. Ask for help if you are unsure what happened.

Make it easy for your friends and family to do the same. A friend group or household where someone can say “I think I’ve made a mistake” without being ridiculed is better prepared to deal with one.

In summary, you don’t need to distrust everything or become a technical expert. You just need a few dependable habits that still work when you are busy, worried or distracted.

  • Slow down when you feel rushed. Pressure is a reason to check before acting.
  • Check through a route you trust. Open the app yourself or call a number you already know.
  • Make protection routine. Use unique passwords, multi-factor authentication and automatic updates.
  • Prepare to lose access. Keep recovery details safe and maintain backups you can restore.
  • Speak up quickly if something goes wrong. Getting help matters more than avoiding embarrassment.
Everything that is happening now has happened before

While looking through old notebooks, I found this piece that I wrote in 2014 for a book that never got published. Reading it through it surprised me how much we are still facing the same challenges today as we did four years ago. Security awareness and security training are no different…

So, you have just been given responsibility for your company’s information security awareness programme and you have rolled out an off the shelf training product to the company. Job done? Probably not unfortunately, because like so many things in security, there is far more to an education and awareness programme than meets the eye. The following nine areas presented here are intended to give you guidance when establishing or improving your programme. Some may not be relevant to your organisation, some will be very relevant, but all of them are intended to provide ideas and insight into what is often a very emotive and personal subject.


Start at the Top

No business programme, least of all a security awareness one, is going to have any ongoing impact in an organisation if it doesn’t have the full support the senior leadership. Depending upon the type and size of organisation this could be the Board, the senior management team or even the C level executives.

Be wary of them just paying lip service as well, as they are crucial for the ongoing engagement of the company and your programme’s success. If they are the ones that haven’t taken their training then they are not committed to your programme. Senior leadership should be helping to not only communicate the training, but also reinforcing key messages and certainly leading by example.

Finally, make sure you can report back the senior leadership on the value of the training on a regular basis, be it every three, six or twelve months. However you choose to do this, bear in mind that the key purpose is to ensure your awareness programme is aligned with the business goals, and that is seen as a part of your organisations continued success.

Don’t Rely on Compliance

Using compliance as a key driver for acquiring investment for an education programme does work, but it is a short sighted approach that will limit what you can do in the future. This is because compliance is a very specific business problem that awareness addresses, and when the compliance requirement has been met there is no reason for the business to invest more money, investigate alternative approaches or expand the programme. That tick in the box limits the future of your programme.

Instead, use compliance as just one of the many drivers to build your programme, along with profit retention, reputational damage control and a protection against lost billable time for instance. These drivers will help your programme, again, align better with the company’s goals.

Teach Them to Fish

Now onto the content! No training is going to be able to put across the correct response to every single threat, every single implication of regulations and laws, and every single type of social engineering approach. The goal of the training is to arm people with a mindset, not all the answers.

Educating people on the implications of their actions, and not their actions alone is key here. By understanding that clicking on a link could result in something bad happening is more effective than just telling them not to click on links. Helping them appreciate that social engineers use an array of techniques to build a picture of the environment is more important than telling them to mistrust every interaction with every person they interact with.

In your position as an InfoSec professional, how do you know when a link or a question is dangerous? Try to put that across, and you should end up with an awareness programme that educates people not programs them.

Make it Relevant

Off the shelf awareness programmes are often seen as a quick, cost effective and easy approach to educating people. Many of the courses are very good too. However, you should be aware of your own organisational culture. Large, regulated organisations probably couldn’t effectively train through regular lunchtime briefings, and smaller organisations probably wouldn’t receive too well being in a room for three hours and having a PowerPoint shouted at them.

Additionally, there are going to be activities, lexicon and even teams and roles that are unique to your organisation. Try and avoid people having to “translate” the training they are taking to be relevant to their daily lives as much of the impact of the training will be lost.

Make it Useful

Not only should the training be useful in someone’s working lives, but also in their personal lives. In a world of Bring Your Own Device (BYOD) the lines between the workplace and home are increasingly blurred, and home networks, tablets and computers are increasingly being used to deliver into the workplace.

Educating people on how to secure their home network and WiFi, how to use a VPN in a cafe with their personal laptop, and even how to manage their own online lives not only helps secure the workplace, but also gives them a sense of being valued for the contributions they are making to the organisation.

Don’t be Too Serious

Humour is always an awkward subject when it comes to education and awareness, as it is rarely a universally agreed topic. However it is worth bearing in mind that given the often large amounts of “compliance” training often required these days (ethics, anti bribery, harassment etc training) making your course stand out is important.

Wherever possible draw upon the culture of the organisation, use in-house references (so everyone understand them) and try and avoid obscure internet humour as many people in the workplace may not understand it. Never, ever use offensive humour, or even anything that comes close to it. If your grandparents are unlikely to laugh then don’t use it!

Go MultiChannel

Taking a leaf out of the book of the marketeers and advertisers, your awareness program should be multichannel and use a number of different approaches to ensure the message gets across. Consider using videos wherever possible, leaflets, internal blogs, “sponsoring” internal events, using town halls and company meetings to present on specific security awareness projects. Poster campaigns are also a useful method of putting core concepts and points across, although a key part to their success is that they get changed on a regular basis to avoid becoming blind to them over time.

Also consider branding items like stickers, pens and pencils with a tagline or advice that ties in with your overall campaign in order to keep your security message in regularly being reviewed. Again this depends very much on the culture of your organisation as to what may seem like a cheap gimmick versus a good idea.

The core concept with this is to constantly engage with people through different means to maintain their attention and recollection of your security training.

Confirm Their Understanding

Making sure people actually understand the fruits of your hard labour goes beyond asking ten banal and blindingly obvious questions at the end of the training. These questions are table stakes when it comes to meeting compliance requirements but do nothing for actually confirming understanding. Conducting social engineering tests, sending false phishing emails (a whole topic in of itself) and even leaving trackable USB sticks lying around are valid ways to test peoples knowledge. The results of these tests can be written up providing even further educational opportunities in articles for the intranet and email updates.

Get Feedback & Start Again

The only way your awareness programme is going to improve over time is to ensure you gather open and honest feedback from all of those that you engage with throughout every phase of your involvement in your security awareness programme. Feedback from all of the recipients of the training, after every talk or awareness session and certainly feedback from the overall programme on an annual basis is an important way of ensuring good elements are enhanced and bad elements are removed.

Gathering feedback however is only half of the story; providing feedback on the effectiveness of the security awareness programme to senior leadership is also important. Consider metrics and the correlation of elements of the training as they roll out over the year to reported security incidents. Wherever possible do you best to monetise the incidents in terms of cost to the business so that over time, as security incidents decline (which they should do!) you can demonstrate the value of the programme and its contribution to the business.

Not all of these may be applicable to you and your organisation, but they should provide some guidance and ideas for you and your security awareness programme.


Ground Control to Major Thom

I recently finished a book called “Into the Black” by Roland White, charting the birth of the space shuttle from the beginnings of the space race through to it’s untimely retirement. It is a fascinating account of why “space is hard” and exemplifies the need for compromise and balance of risks in even the harshest of environments.

Having seen two shuttles first hand in the last nine months (the Enterprise on USS Intrepid in New York and the Atlanta at Kennedy Space Centre), it boggles my mind that something so big could get into space and back again, to be reused. Facts like the exhaust from each of the three main engines on the shuttle burn hotter than the melting temperature of the metal the engine ‘bells’ are made of (they ingeniously pipe supercooled fuel down the outside of the bells to not only act as an afterburner of sorts but also cool the bells themselves) go to show the kind of engineering challenges that needed to be overcome.

There was one incident however that really struck me regarding the relationship between the crew onboard and the crew on the ground. On the Shuttle’s maiden flight into space, STS-1 also known as Columbia carried out 37 orbits of the earth with two crew on board, mission commander John W. Young and pilot Robert L. Crippen. Once orbit was achieved an inspection of the critical heat tiles on the underside of the shuttle showed some potential damage. If the damage was too extensive the return to earth would (as later events in the Shuttle’s history proved) be fatal.

The crew however were tasked with a variety of other activities, including fixing problems onboard they could address. They left the task of assessing and calculating the damage to those on the ground who were better equipped and experienced to deal with the situation. This they duly did and as we know Columbia landed safely just over two days later.

It struck me that this reflects well the way information Security professionals should treat the individuals we are tasked with supporting. There is much that individuals can do to help of course, and that is why training and awareness efforts are so important, but too often it is the case that “we would be secure if it wasn’t for the dumb users”. The sole purpose of the Columbia ground crew was to support and ensure the safe return of those on board STS-1 so that they could get on with their jobs in space. Ours is the same.

Just because te crew had extensive training to deal with issues as they arose, the best use of their time was to focus on the job in hand and let ground crew worry about other problems. The people we support should also be trained to deal with security issues, but sometimes they really need to just get on with the deliverables at hand and let us deal with the security issue. They might be trained and capable, but we need to identify when the best course of action is to deal with their security issues for them, freeing them to do their work.

Never forget that we support our organisations/businesses to do their jobs. We provide tools to allow them to be more effective in their end goals but it is still our responsibility to do the heavy lifting when the time comes. Except in very rare cases we are there because of them, not in spite of them.

(Photo courtesy of William Lau @lausecurity)


“And the winner is… Compliance!”

real-men-real-men-demotivational-poster-1221782347Disclaimer: My comments below are based upon quotes from both Twitter and The Times of London on the UK’s TalkTalk breach; as a result the subsequent investigation and analysis may find that some of the assertions are in fact incorrect. I will post clarifying statements should this happen to be the case.

I am not normally one to pick over the bones of company A or company B’s breach as there are many people more morbid and qualified than me to do so, and I also hate the feeling of tempting fate. All over the world i would guarantee there are CISOs breathing a sigh of relief and muttering to themselves/psychoanalyst/spouses “thank god it wasn’t us”. Bad things happen to good people, and an industry like ours that tends to measure success on the absence of bad things happening is not a great place to be when those bad things appear to happen far more frequently than ever before.

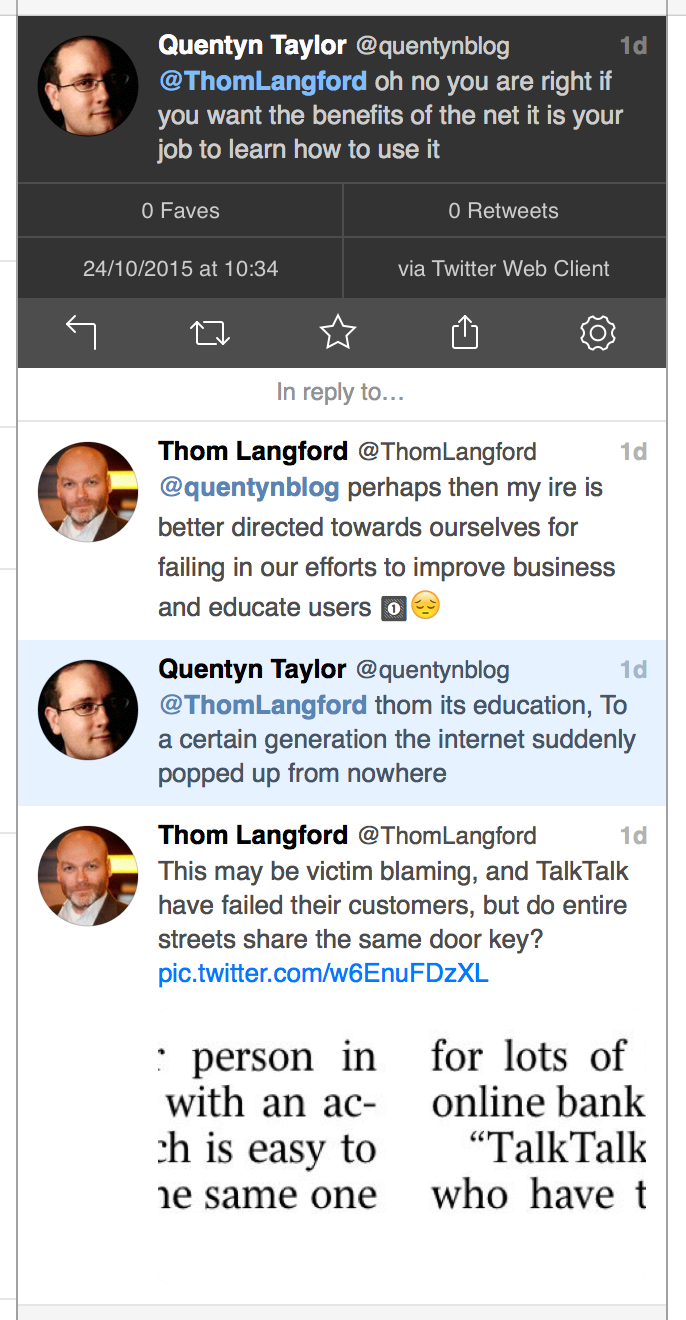
So it took me a while to decide if I should write up my feelings on TalkTalk’s breach, although I had Tweeted a few comments which were followed up on.

Quentyn W Twitter 1

(that original quote I Tweeted from the Times)

that original quote I Tweeted from the Times dated 25th October 2015

Initially I was shocked that people are still using the same password across so many crucial accounts. After a ten minute rant in the car about it with my wife, she calmly (one of the many reasons I married her) explained that not everyone thinks like me as a security professional, and that I should remember my own quote of “convenience eats security for breakfast”. Having calmed down a little, I was then shocked by something else.  That something else was when the TalkTalk CEO, Dido Harding was on national television looking clearly exhausted (I can only imagine how much sleep she had been getting the last few days) giving out unequivocally bad advice such as “check the from address on your emails, if it has our address it is from us”. Graham Cluley’s short analysis was spot on here:

As if TalkTalk’s customers hadn’t gone through enough, they are then being given shoddy advice from someone in a supposed position of trust that is going to put them at even more risk. The scammers and phishers must have been rubbing their hands with invisible soap and glee as they prepared their emails and phone calls.

Now, the attack it seems did not disclose as much information as was first though, which is good news. So credit card numbers were tokenised and therefore unusable, so no direct fraud could be carried out there (again dependent upon the form of that tokenisation which I am sure there will be more details on in the coming months). Bank details were however disclosed, but again, there is a limited amount of damage that can be done there (there is some I acknowledge, but it takes time and is more noticeable… another time for that discussion). Here is the Problem Number One though; with Harding’s poor advice, many people subsequently (and allegedly) fell for phishing attacks through either phone calls or emails, and lost hundreds of thousands of pounds. TalkTalk’s response? Credit monitoring.

And then we move to Problem Number Two; Why weren’t the bank details stored safely? Why were they not encrypted? Armed with the knowledge of customers bank account details scammers can make a much more convincing case that they are actually from TalkTalk, especially if other account information was also lost (time will tell). TalkTalk’s response?

TimesTalkTalk

Dido Harding talking to The Times, 24th October 2015

So TalkTalk was technically compliant? Shouldn’t this kind of thinking be consigned to the same mouldering scrapheap where “we’ve always done it this way” and “we’re here to secure the business, not help it” lay? I sincerely hope that this episode will at the very least highlight that “compliance” and “security” are two very different things and that the former most certainly doesn’t automatically result in the latter. What has transpired is the perfect storm of a breach, unforgivably poor advice, and complacency based upon compliance and resulted in the pain of a lot of people involving large amounts of money.

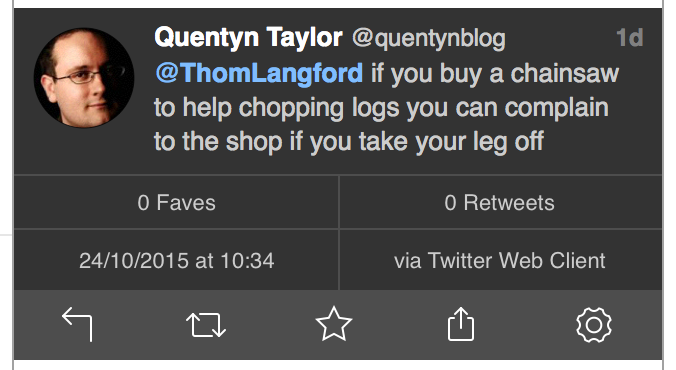
If an example like this does not spur you into doing more as regards your own security awareness activities, then please go back to the beginning and start again. Why? I have been accused of “victim blaming” somewhat (see the above Tweets), but if individuals had an ounce of sense or training they wouldn’t have fallen for the subsequent scams and been more careful when responding to email supposedly from TalkTalk. I will leave the last word to Quentin Taylor, and as you carry on with your internet residencies, don’t forget you need to wear protective clothing at all times.

Quentyn W 2


Making the world angrier, one process at a time

Angry Thom BlogI have recently set up Family Sharing on my iOS devices, so that I can monitor and control what apps go on my kids devices without having to be in the room with them. Previously they would ask for an app, and I would type in my AppleID password and that was  that. Unfortunately with my new role I am travelling so much now that the thought of waiting a week before they can get an apps was causing apoplectic grief with my kids. Family Sharing was the solution, and when I had finally worked it out, we were goood to go and it works well. I can now authorise a purchase from anywhere in the world. I get woken up at 3am with a request for a BFF makeover or car crash game (one girl, one boy) but my kids are happy.

One problem however was that for some reason my daughters date of birth was incorrect, therefore indicating that she was an adult, and thereby breaking the whole “app approval” process. Straightforward to fix? Not at all.

I won’t bore you with the details, but it was the most frustrating process I have encountered in a long time. I admit, I misinterpreted the instructions along the way (they were a bit asinine in my defence), but it came down to the fact that I had to have a credit card as my default payment method for my family account, not a debit card, simply to authorise the change of status of my daughter from an adult to a child. In other words, I had to jump through hoops to restrict her  account rather than give it more privilege. Not only that, but from an account that already had the privileges in the first place. There didn’t seem to be any element of trust along the way.

I am sure there is a good, formal response from Apple along the lines of “take your security seriously”, “strong financial controls” etc, but as an experience for me it sucked, and if I could have worked around it I would have. Thankfully not all of Apple’s ecosystem works like this!

This is a problem for many information security organisations when they introduce procedures to support organisational change or request mechanisms. For instance, how many times have you seen a change request process require CISO, CIO and potentially even higher approvals for even simple changes? Often this is due to a lack of enablement in the organisation, the ability to trust people at all levels, and often it is a simple lack of accountability. It seems we regularly don’t trust either our own business folks as well as our own employees to make the right decisions.

Procedures like this fail in a number of places:

  1. They place huge pressure on executives to approve requests they have little context on, and little time to review.
  2. The operational people in the process gain no experience in investigting and approving as they simply escalate upwards.
  3. The original requestors are frustrated by slow progress and no updates as the requests are stuck in senior management and above queues.
  4. The requestors often work aroun d the procedure, avoid it, or simply do the opposite of what finally comes out of the request as work pressures dictate a quicker response.
  5. The owners of the procedure respond with even tighter regulations and processes in order to reduce the ability nof the nrequestor to wotk around them.

And so the cycle continues.

The approach I have regularly used in situations like this comprises of two tenets:

  1. Consider the experience of the user first, then the desirable outcomes of the process second.
  2. Whatever process you then come up with, simplify it further. And at least once more.

Why should you consider the expoerience of the user first? Who is the process for the benfit of, you as in formation secuity, or them as the end user? If you answered the former, then go to the back of the class. We are not doing security for our benefit, it is not security for the sake of security, it is to allow the user, our customers, to do more. If we make their experience bad as they do their best to make more money, sell more beer, do more whatever, security becomes an irellevance at best and a barrier to successful business at worst.

Making the requstors exoerience as painless and as straightforward as possible (perhaps eeven throw in a bit of education in there?) they are encouraged to not only see the long term benefits of using the procedure as we defined, but also become fanatical advocates of it.

Secondly, why should we keep it simple? Well not only to support the above points, but also because guess who is going to have to support the process when it is running? Of course, you and your team. If the process itself is bulky and unmanageable then more time will be spent running the process than doing the work that the process needs to support. If that amount of time becomes too onerous over time, then the process itself breaks down, the reporting on the process becomes outdated, and ultimately the process itself becomes irrelevant and considered a waste of time by those it affects.

Putting your requestors at the centre of your simplified process universe will always make that process more robust, more understood, more beneficial and of course more relevant to the business, and who can argue with that?

InfoSecurity Europe

I spoke at this years InfoSecurity Europe in London a few months back on articulating risk to senior management. Peter Wood, the moderator, did an excellent job as moderator of the panel, and even revitalised my faith in them after too many very poor experiences earlier this year.