Woof Woof, Bark Bark (or how to not support security in your organization).

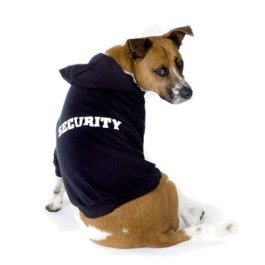
security_dog_hoodie_on_black_whiteI recieved the email below from a colleague at work. At first glance it is funny, the chief security officer being represented by a dog… Hilarious! Of course security is just about being able to bark at people and occasionally bite them. This role isn’t about corporate responsibility or even enterprise risk management, it is about wagging your tail and barking at people and getting them to do things because you have barked it so.

I’m having second thoughts about my growth plan if this is where it leads to.

CSO dog

If I am honest, I am guilty of this too. I have often described myself as an “overpaid security guard” to people who haven’t a clue about information security, and they nod knowingly at me, thinking they understand InfoSec policy, enterprise risk and even DLP.

The above example of belittling the security function of an organisation has steeled me into action; if I can’t explain the role of a CISO/CSO to my Mother, then I need to re-evaluate what it is I am doing and the impact it has on the business. It also annoys me that the role of CISO is so easily belittled. I don’t think I have ever seen a CFO role boiled down to an image of a coffee bean, or even the CIO image reduced to a mouse or keyboard. What makes this worse is that this product offers “the highest security for your files in the cloud” and yet this is how seriously they take security.

A fundamental part of this is down to us as CISO’s and security people to ensure we don’t belittle ourselves to ingratiate ourselves. It is extremely difficult for us to ensure we are valued and respected in our organisations as it is, and sometimes the somewhat subservient/comedic route feels easiest. This is not the best way; it is the longest and hardest route to acceptance and understanding because the role is by it’s nature seen as a frivolity and a hilarious side act.

(We should note however that there is a place for humour in security, and if used correctly it is extremely effective. The point I am making above is that security as a serious subject should not be presented as a humourous aside.)

I recall a situation where I noticed someone working at a hot desk who had no visible identification. I asked around if anyone knew who the individual was, and nobody did. As I approached the individual I was met with a chorus of “get him Thom” and “tackle him mate!” etc. with much hilarity ensuing. None of it was meant meanly of course, but it was synonymous with the  simplistic attitude of security. If any of the people who had spoken those words had any real idea of the security implications of having someone in their office without any idea of who they are, then their response may have been a bit more serious. The best part is of course that I had plainly failed in my security education and awareness with this group of people.

We are not guard dogs. We are not security guards (although they are an important part of the security function). We are not bouncers. We are not doing security for theatrical effect.

We are here to protect your revenue, your reputation and your bonus payouts. We are here to ensure we maintain good relationships with our clients, and allow our organisations to take on greater risk and therefore reap greater reward. We are here to help inform the business of security risk and advise as required.

What’s so funny in that?

Note: I have been extremely quiet on here these last few months; my role has changed dramatically at work requiring more travel and less time for the frivolous acts of blogging. Combine that with a busy schedule with Host Unknown and my other info sec commitments I have neglected this blog site somewhat. Hopefully this post sees me back in the saddle again, and you can always catch up with me on Twitter. Oh, and the holiday was good too!
ThomLangford_2014-Aug-10

ThomLangford_2014-Aug-10 1


If It is Too Good To Be True, It Probably Is – Cross Post

(Originally Posted on Information Security Buzz on 15 January 2014)

There are plenty of tips on the internet that give great advice on how to avoid phishing scams, and there will be other authors on this site that will be giving very similar advice. For me though, it always comes down to the following three thoughts that I keep in mind whenever I see an email that could possible lead to a scam.

1. Is it too good to be true?

Infosecurity-Buzz-January-2014.002.jpg.001-300x168If the email in question is offering me something for nothing, especially if there is money, or a monetary value involved, this type of email falls into the “too good to be true” category. I have yet to come across an example of when someone really was giving away iPad’s, cash or holidays without some kind of quid pro quo involved. If your answer to the above question even looks like it might be a “yes”, the email and its contents can probably be ignored.

2. Don’t Click it!

Infosecurity-Buzz-January-2014.002.jpg.002-300x168I have borrowed this particular phrase from Jaded Security who coined it a few years ago, and I like it because to be honest it is simple and memorable advice. There are nuances to this of course, but unless you are experienced just don’t click links in your email (see number three). As you get used to looking out for this kind of email there will of course be other telltales that will help you know if an email is genuine or not. For instance, is the email from a close friend, but they haven’t addressed you by your nickname, and seem to be oddly formal, or have more spelling mistakes (or even not enough) in their message? It could be that they have been compromised and you are in their address book and therefore being targeted.

Some people regularly send links in emails, others almost never; if that’s the case, ask yourself why they have suddenly started today seining you a link to a sneezing panda clip.

Finally, if your bank sends you a link to change your password because of system upgrades, don’t click the link they send, but go to your usual bookmark for them. Your bank should never do this anyway, but clicking on a link in an email like this is almost guaranteed to not send you to your bank, but a very convincing fake site set up to harvest your usernames and passwords. Just don’t click it.

3. Fail Safe

Infosecurity-Buzz-January-2014.002.jpg.003-300x168It is always better to mistake a genuine email for a scam rather than the other way around. The consequences of clicking something are very serious whereas the consequences of not clicking on the attached link are rarely, if ever, serious. Additionally, if it is a genuine request, the sender is likely to send a reminder or contact you through another medium such as SMS, letter or telephone. Of course there are plenty of scams through these mediums too (another topic perhaps?), but you will have the balance of probabilities on your side, and the knowledge you haven’t done anything stupid.


A Christmas Public Service Announcement

I have known the good folks of Twist and Shout for a few years now and think their approach to information security awareness and education is spot on. Using good production values, great scripting and where appropriate some humour they have made some great short films. I have been fortunate enough to use some in my own presentations as well.

I am thrilled to be playing a part in their latest Christmas viral in collaboration with another project I am involved in, Host Unknown. I hope you enjoy it.

(It also explains why I have been sporting a beard for the last few weeks.)


What’s this security stuff for anyway?

I am currently sitting in the BA lounge in Heathrow awaiting a flight to Delhi, and as I look around at the number of laptops lying around it reminded me of something I saw a few years ago at Delhi International Airport as I was waiting to fly back to the UK. It was so shocking I even used it as an example in a security article I wrote for my company on my return. Regular readers will know that I have a thing about unattended laptops anyway as it  has the potential of negating all of the technical measures put in place in certain circumstances. Anyway, I decided to write it up here as an example (and of course to kill the time in the lounge!).

It was about midnight, and I was in the BA lounge (sometimes shared with other airlines), and it was quite a busy evening so most of the seats were taken.

I was sat next to a gentleman who opened up his laptop and switched it on. It immediately asked for a password, I presume for the on disk encryption. He then had to log into his account, and then finally he connected his own data card (no local WiFi and inherent insecurities for him!) and subsequently connected to his corporate VPN using a username, password and an RSA two factor authentication token. All good stuff from a security perspective.

I noticed from his wallpaper logo right in the centre of his screen that he worked for an aeronautics defense contractor, so the level of security didn’t surprise me. What he did next however did…

After successfully connecting, he placed his laptop on on the table in front of him and went to the toilet… without even locking his laptop. He was away for 15 minutes.

I was so shocked I even took a photo of his laptop which is attached – this is honestly the laptop in question! If you look carefully you can see the window with his VPN connections in the middle of the screen

image

It summed up to me that even though there was all of this security on his laptop, it was rendered useless by his carelessness and utter disregard (or utter lack of awareness) of the security of the contents on his laptop. He entered the passwords that protected his data because that was what he needed to do to get his job done, not because he understood what it was for.

When we overcome scenarios, attitudes and understanding that results in this kind of thing being played out the world over, we will have addressed a huge amount of risk in our industry.

Bon voyage!


Why I am an Analogies Project contributor

Bruce_Hallas-300x286That devilishly handsome bloke you see to the right is Bruce Hallas. I used to go to school with him nearly 25 years ago, and then last summer, at the first old boys school reunion that our year organised since leaving I met him again, and it turns out we are in the same infosec business. I spoke to him about all of the good work I am doing, the company I work for, the many countries I visited and generally tried to make myself feel more important than the skinny eighteen year old I was when I last saw him. He told me that he runs his own infosec consultancy, his own blog, works with the UK government, and was in the process of setting up “a project” as a freely available, self funding, resource of analogies/stories to help people better understand information security. (Bruce immediately won the “my life is awesome since leaving school” competition of course.)

Since that time, The Analogies Project has grown from one man, an idea and a website to something producing real, quality content, and with a very promising and bright future.

In the words of the Project itself;

The Analogies Project has a clear mission. To tackle the unintelligibility of information security head on and secure the engagement of a much broader audience. Its aim is to bridge the chasm between the users, stakeholders and beneficiaries of information security and those responsible for delivering it.

Through a series of innovative initiatives the Analogies Project will enable information security professionals to effectively communicate with their chosen audiences. The content will be delivered through a variety of alternative communication techniques, media and partners.

The part of this project that I like the most is that it is essentially a community project. Bruce isn’t charging money for membership to the analogies as they are written (and they are coming thick and fast now!), and none of the contributors are charging for their work either. There are not only the web contributions in the form of a library, but a book planned, a conference, and even an opera! With the momentum that is currently behind the project at the moment there is every reason to believe in its future success.

So why am I contributing? Honestly, I have selfish and philanthropic reasons to do so. Obviously it gets my name out there, allows me to practise my writing, test some ideas and also say “I was there from the start”. All that aside though, I have frequently struggled in my day job to get infosec concepts across to people, either directly, in meetings or even in awareness training. To have had a resource like this available to me five years ago would have made my life so much easier, allowed me to advance the infosec “cause” more effectively and given me a set of tools I knew were consistant with the prevailing thoughts of industry commentators. Having a centralised, peer validated, toolkit available is fundamental to us as professionals when it comes to the messaging we give to our users, clients, bosses, teams and even the infosec community as a whole.

It’s still early days, but I have submitted my first contribution just last week (soon to be published I hope) and I am already inspired enough to be working on my second and third. There are a number of analogies already in place, and I would urge you to read them and consider them in the context of your current communications to your audiences, whomever they may be.  The book will be another important milestone and one I hope to play a part in; indeed I hope to be able to play a part in the the project for the forseeable future, and why I am happy and proud to display my “contributor” badge up on the top right of this site.

TAP-Contributor-Semi-Transparent-250x160

If you feel you have something to contribute, then head over to The Analogies Project and let Bruce and the organisers know. If you don’t feel ready to, then certainly check it out anyway. You won’t regret it.