Attitude, Knowledge, Opinion and Expertise; an information security career map?

opinionI was talking to one of my colleagues a few days ago who joined our team a little under a year ago. Althea (I promised her a name check here) actually joined the security team from the small group of personal assistants in the company. While this is perhaps not the most obvious place to recruit into a technically savvy environment from, Althea has very quickly become an excellent member of the team.

I often hear in conferences and panels about the security skills shortage we are currently suffering, and I regularly quote the story of Althea joining us as an example of how we are very often simply looking in the wrong places and should be looking to promote from within more. Althea has been with the company for six years (a long time these days) and was working for and supporting some of the most senior people in our company. She had to be organised, forthright, able to communicate succinctly and above all remain calm under pressure (you know how senior executives can be sometimes).

For me, her attitude is far more important than her technical ability. Technology and hard skills are things that can be taught in relatively short periods of time; attitude is something that takes a lot longer to learn, decades even. Althea is already well on her way to getting the requisite technical skills required of her role, but her organisational skills, contacts within the organisation, and ability to communicate to people throughout the organisation whatever their seniority is second to none.

I was talking to her about this and related the competence framework I use to try and understand both mine and others maturity in their role. When first moving into a new role you move through each of one of these phases of competence:

  • Unconsciously Incompetent
  • Consciously Incompetent
  • Consciously competent
  • Unconsciously competent

(you might want to reread those a few times, I know I did when I first came across them)

So, if you start with the right attitude, you are going to minimise the amount of time you spend being unconsciously incompetent, as the next logical step is to acquire knowledge. This allows your to bring the right skills to bear onto your role, and bring you quickly into being consciously incompetent and possibly beyond. Minimising the time you spend in the first two phases is of course very important to your career.

But knowledge really isn’t everything. Those with just the knowledge can’t see beyond their day to day tasks and roles; they are unable to see the “big picture” as everything is focussed around technical solutions and black and white answers to business problems. (Just listen to some of the “questions” asked at every security conference you go to; they are not really questions but affirmation that their knowledge is greater than the speaker. They wholly miss the point that knowledge is actually all they have.) I would suggest that forming your own opinions on subjects is a logical and vital step in anyone’s career path. Business problems are not black and white, there are a variety of approaches, solutions, outcomes and inputs that those with a purely knowledge/technical viewpoint simply won’t appreciate. Forming and gathering these opinions takes place through reading, observing, listening, writing and finally testing your opinions in the community. These experiences are not just the gathering of specific knowledge, but the nuances of what can be right in one circumstance, wrong in another and even every possibility in between.

For instance, shipping a single, failed drive that was part of a RAID 5 cluster back to the manufacturer may be the right thing to do for some organizations. From a security knowledge perspective this is anathema unless the drive has been degaussed or even fully destroyed; it completely depends on the business, circumstance and many other factors. Encrypting backup tapes? Obviously this should be done, except of course when it shouldn’t, for the same reasons as before. Security is only one opinion in a sea of opinions that matter.

Having opinions in this industry is vital to stimulate conversation and evolve our understanding and viewpoints in our own workplaces. Once this opinion is applied in a considered and effective manner, only then could one possibly consider themselves having “expertise”, and I wouldn’t label yourself that before someone else does first.

In order to allow your team to grow in this manner it is vital to encourage them to engage with both the internal company community as well as information security community as a whole. Encourage them to take part in any related event, internal and external, or even organise one. What about volunteering to help at a conference, or ultimately even apply to speak? By giving your team members the opportunity to research, write, precis, deliver, defend and receive feedback on a topic of their choice they have the best opportunity to take their knowledge beyond the day to day and into the more opinion based level of the strategic, and become better decision makers in the process.

Why >WE< must meet the demands of the business

At the recent RSA conference in San Francisco, David Spark asked the question “Why doesn’t the business align better with security?” and there were some interesting responses:

I actually only agreed with the last comment from Michael Farnum (whom I have followed on Twitter and finally got to meet for the first time at RSA… see “bald men of security” in my RSA roundup). He rightly says that that the business should not align with security, as it is the role of security to align with the business. Compare this to the question “Why doesn’t the business align better with IT?” or “Why doesn’t the business align better with HR?” and the question immediately becomes moot.

levelI think David was right to ask the question because it has uncovered with greater clarity something that I and many other have been talking about for some time now, namely that security for too long has been carying out secrurity for its own sake rather than supporting the business achieve its goals. In my own paraphrased words “this is what I need security to do to help me sell more beer“.

This was reiterated by Andy Ellis at a session at RSA where he said precisely this;

are you the conscience of the business or an enabler to the business?

Finance is there to provide money, make that money work more effectively and ensure the money is providing the best value for the good of the business. IT is there to provide technology services at the best possible value for the good of the business. HR is there to provide people, support them, nurture them and align them (or move them  out), for the good of the business.

What is your security programme doing for the good of the business, rather than the good of security? Asking this question alone will help you along to your business goals and actually help them achieve their goals, not yours.


If It is Too Good To Be True, It Probably Is – Cross Post

(Originally Posted on Information Security Buzz on 15 January 2014)

There are plenty of tips on the internet that give great advice on how to avoid phishing scams, and there will be other authors on this site that will be giving very similar advice. For me though, it always comes down to the following three thoughts that I keep in mind whenever I see an email that could possible lead to a scam.

1. Is it too good to be true?

Infosecurity-Buzz-January-2014.002.jpg.001-300x168If the email in question is offering me something for nothing, especially if there is money, or a monetary value involved, this type of email falls into the “too good to be true” category. I have yet to come across an example of when someone really was giving away iPad’s, cash or holidays without some kind of quid pro quo involved. If your answer to the above question even looks like it might be a “yes”, the email and its contents can probably be ignored.

2. Don’t Click it!

Infosecurity-Buzz-January-2014.002.jpg.002-300x168I have borrowed this particular phrase from Jaded Security who coined it a few years ago, and I like it because to be honest it is simple and memorable advice. There are nuances to this of course, but unless you are experienced just don’t click links in your email (see number three). As you get used to looking out for this kind of email there will of course be other telltales that will help you know if an email is genuine or not. For instance, is the email from a close friend, but they haven’t addressed you by your nickname, and seem to be oddly formal, or have more spelling mistakes (or even not enough) in their message? It could be that they have been compromised and you are in their address book and therefore being targeted.

Some people regularly send links in emails, others almost never; if that’s the case, ask yourself why they have suddenly started today seining you a link to a sneezing panda clip.

Finally, if your bank sends you a link to change your password because of system upgrades, don’t click the link they send, but go to your usual bookmark for them. Your bank should never do this anyway, but clicking on a link in an email like this is almost guaranteed to not send you to your bank, but a very convincing fake site set up to harvest your usernames and passwords. Just don’t click it.

3. Fail Safe

Infosecurity-Buzz-January-2014.002.jpg.003-300x168It is always better to mistake a genuine email for a scam rather than the other way around. The consequences of clicking something are very serious whereas the consequences of not clicking on the attached link are rarely, if ever, serious. Additionally, if it is a genuine request, the sender is likely to send a reminder or contact you through another medium such as SMS, letter or telephone. Of course there are plenty of scams through these mediums too (another topic perhaps?), but you will have the balance of probabilities on your side, and the knowledge you haven’t done anything stupid.


Top Five From RSA USA 2014

rsac2014-program-guide-cover-320x407pxI attended the RSA Conference USA last week and was able to witness the chaos, FUD, genuine insight, original thoughts and 25,000 people queueing for a coffee and bagel at 10 o’clock in the morning.

Rather than even attempt to do an end of show round up that other have been able to do far more successfully than me, here are the five things that I remembered the most from the week:

3M Visual Privacy

I still think 3M produce the best privacy filters for monitors, but I have been waiting a long time for technology to catch up and remove the unsightly and easily-left-behind at home piece of plastic in favour of a solution built into the screen itself. Whilst I didn’t unfortunately see that, one of the product managers assured me that this is exactly what the boffins at 3M are currently working on. This is going to be a huge step towards universal and transparent (forgive me) visual security for people using laptops in public places.

MISD_PrivacyFilters_Apple_IMG_ENWW3M also surprised me by demonstrating a pice of software they have designed as well; the known problem with privacy filters is that they only protect you from people looking at your screen from your left or right. From directly behind you they can easily see your screen. The software uses the built in webcam to recognise the users face, and if another face appears in the background looking at the screen, pops up a warning to the user and blurs the screen. To be honest it was a little clunky when I saw it, and it is currently only being developed for Windows, but this is exactly the sort of environment that people working with sensitive information need to “watch their backs” almost literally. I hope they continue to refine the software and expound it to all other major platforms.

Security Bloggers Meetup

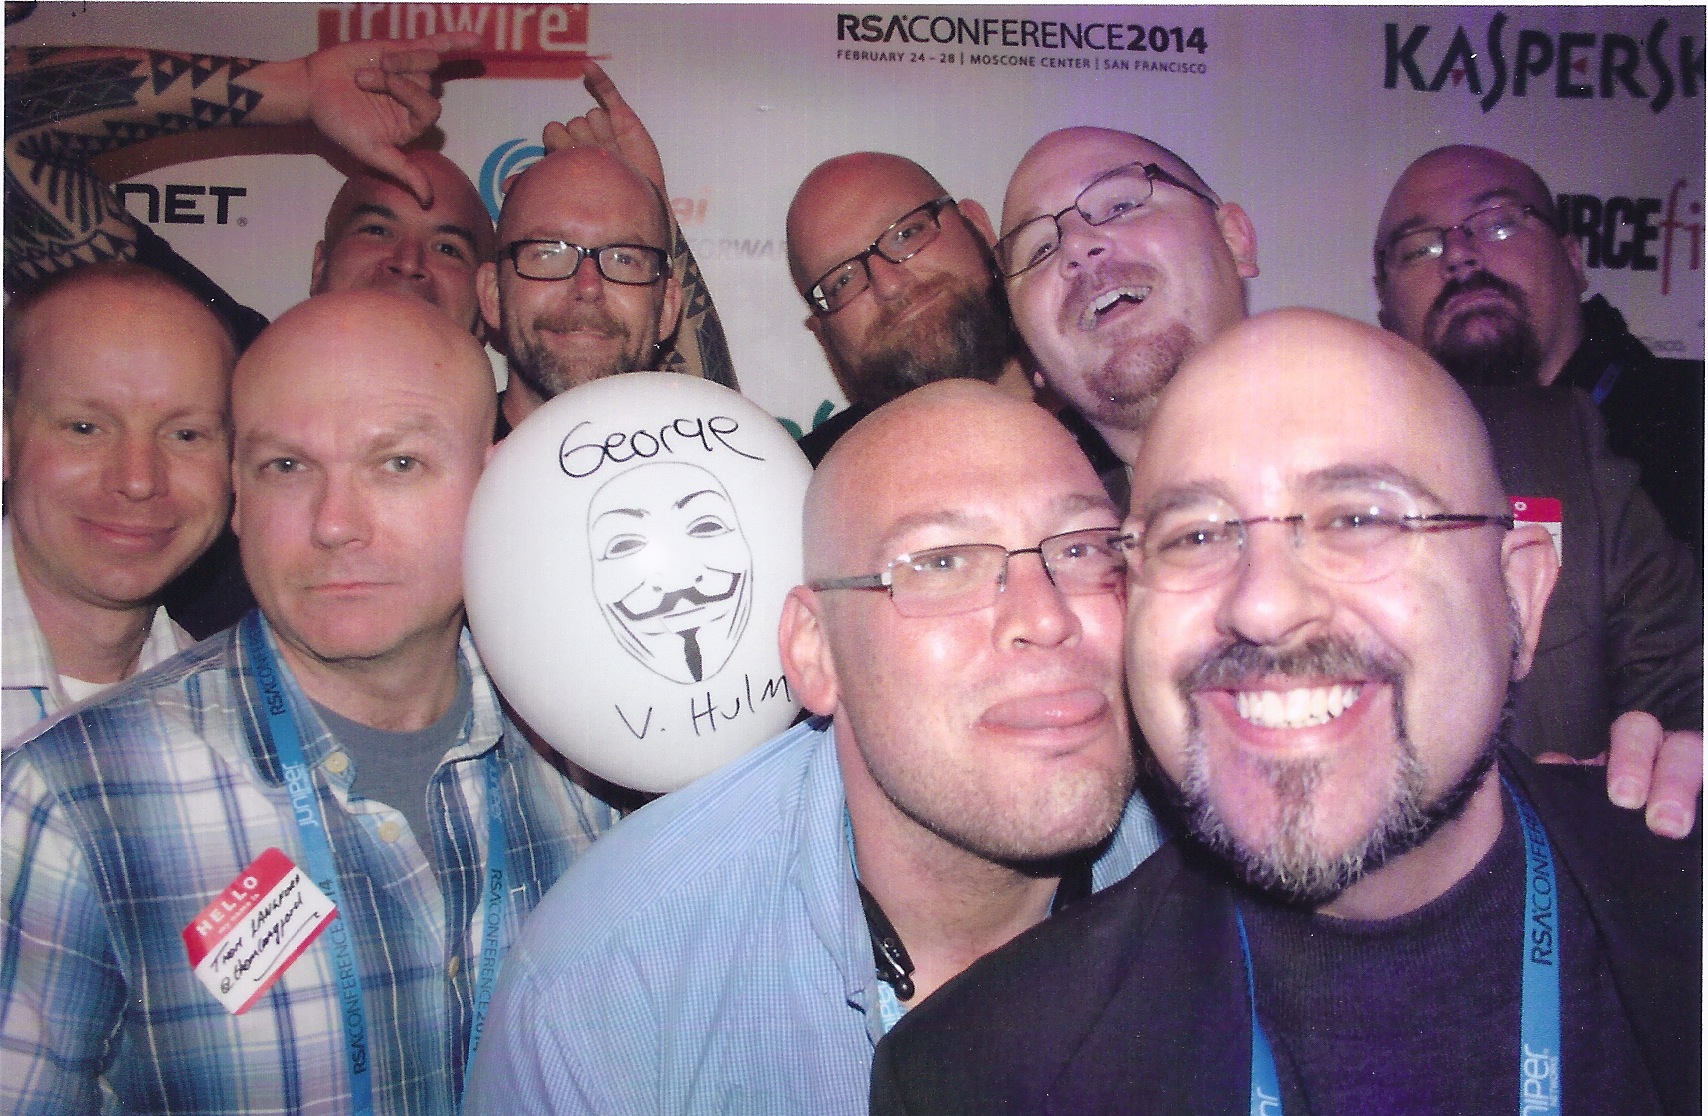
sbnRSAC USA sees the annual meet up of the Security Bloggers Network, so i was very excited to be able to attend this year and witness the awards show and a great deal of silliness and nonsense (to whit, the “bald men of InfoSec” picture for one). I managed to meet for the first time a whole bunch of people that I have either conversed with or followed myself, and some of whom I have very much admired. No name dropping I am afraid as there is too much of that later on in this post, but one thing I did take away was that there is a very valid desire to harmonise the North American and European Security Blogger Awards moving forwards which can only be a good thing and build the international blogger network further. In fact, you can now nominate for the EU Security Bloggers awards here.

The "infamous" bald men of security.

The “infamous” bald men of security.

SnoopWall and Miss Teen USA

snoopwall-website-logoIt wouldn’t be a security conference without some kind of booth babe furore and this one was no different. Although the presence of booth babes has dramatically reduced over the last few years there were still a few vendors insisting on using them. And then we thought we had hit a new time low with the presence of Miss teen USA, Cassidy Wolf, at the SnoopWall booth in the South Hall. Condemnation was rapid and harsh. BUT WAIT… THERE’S MORE TO THIS STORY THAN MEETS THE EYE! After I retweeted my feelings about a teens presence at a conference that could best be described as a recovering alcoholic when it come misogyny, I was contacted by Patrick Rafter, the owner VP of Marketing of SnoopWall.

They have partnered with Cassidy to promote privacy amongst teens in complement to their product that detects the misuse of, for instance, the webcam on your computer or your phone. For those that may not know, Cassidy was the victim of blackmail from an ex classmate who hacked into her webcam in her bedroom, took photos and then demanded more pictures. It goes without saying she stood up to the blackmailer, and has since made privacy one of her “causes” during her tenure as Miss Teen USA. Was having her at their booth at RSA a little misjudged? Yes. Is their cause and campaign (and software for that matter) actually have very good intentions? Absolutely. I chatted with Patrick a day later and while he acknowledged how Cassidy’s presence could have been misinterpreted, he strongly defended her presence and her intentions. I honestly found it laudable. Hopefully over the next few years as the industry finally sorts out its booth babe problem, people like me won’t be jumping to the wrong conclusions as we assume the worst.

The Thomas Scoring System

Thomas Scoring System LogoA few months ago I posted about Russell Thomas’ approach to risk management. I had the good fortune to meet with Russell at the Security Bloggers Meet Up and chatted in depth about his approach to measuring risk consistently. He has turned this idea into a very practical approach via an Excel spreadsheet, a point I made in my earlier review. This is important because without a way to implement at a very practical level it remains a theory. The following day Russell was kind enough to walk me through how to use the system in practical terms, and I am going to be trying it out in my day job as soon as possible. I would urge you to take a look at the Thomas Scoring System as I strongly believe it is a great way of bringing metrics together in a meaningful way.

Gene Kim & The Phoenix Project

I was fortunate enough to have been introduced to Gene Kim, the founder of Tripwire, author, DevOps enthusiast and all round genius/nice guy a few months ago, and we had chatted a couple of times over Skype. (Gene is very generously offering me his guidance around writing a book and his experiences publishing it; yes you heard it here first folks, I intend to write a book!) Knowing he was at RSA I was able to seek him out, and I can now say I have met one of my InfoSec heroes. He is a genuinely charming, funny and generous guy, and he was good enough to sign a copy of his book, The Phoenix project, as well as allow me to get a selfie with him. I would strongly encourage everyone in this field, as well as many of those not in it to read The Phoenix Project, as it quite literally changed the way I looked at the role of InfoSec in a business, and that wasn’t even the main thrust of the book.

Gene very graciously allowing me to take a selfie with him

Gene very graciously allowing me to take a selfie with him

It has taken me nearly a week to recover from RSA, but despite the scandal and boycotts and minor demonstrations it was an excellent conference, as much for the presentations as the “hallway track”. As always, my thanks to Javvad for being my conference wing man again.

Is that Javvad, or a waxwork I am posing with?

Is that Javvad, or a waxwork I am posing with?

Now it is back to real life.


EU Security Blogger Awards 2013

It is not often I am inspired enough to write a post at the breakfast table, let alone on a Saturday, but that is exactly what is happening now. Brian Honan (@brianhonan) just this morning announced the opening of the EU Security Blogger Awards voting.
I had taken the time last week to vote for the nominees for this award as I felt strongly that while there is a strong infosec community in Europe we rarely shout about the fact. I also noticed that many of the blogs and twitter feeds I follow are USA based; nothing wrong with that per se, but as a result I was losing a certain element of relevance in my reading, education and therefore understanding about the issues that affect us in the industry, and specifically in the EU.
With Brian’s announcement I duly voted and todays announcement is the result of that process, namely the nominations for the awards. As a result of this however two wonderful things have come about; firstly, I have been given a rich seam of bloggers and tweeters to follow! This is like being given free textbooks at school, or a free subscription to your favourite infosec magazine. I fully intend to tap this source of information to its fullest extent in the coming weeks.
Secondly, I was both amazed and honoured to have been nominated in the category of Best Personal Security Blog! This is a tremendous surprise and somewhat daunting given the company I am keeping in this category. I am all the more humbled by the fact that this nomination was made possible because of people voting; to those of you who gave your unsolicited vote for me to be in this category, I thank you.
So I would urge all of you who read this to not only look at the nominations at the above link to see who else is out here in the EU blogging space, but also to vote and really underscore the fact that the EU blogging community is large, noisy, vibrant, informed, opinionated and above all active in the information security community. Your cheques will be in the post shortly.